

The summer of 2026 taught the security industry a new phrase: the stolen AI login. In late August, as BleepingComputer reported, Anthropic responded to infostealer-driven hijacking of Claude sessions by signing users out, wiping saved payment methods, and refunding charges it identified as unauthorized.
That is the supply side. SOCRadar’s AI Identity Exposure Report goes after the demand side: the enterprises whose employees are the credentials being sold.
Starting from more than one million infostealer records tied to AI services across 80,000-plus corporate domains, the research narrowed the set to 482 major established enterprises to answer a single question: when an AI login lands in a stealer log, whose is it, and what does the buyer inherit?
Of the 482, 68% are billion-dollar organizations across 36 countries and eight sectors, concentrated in North America, dozens of them Forbes-ranked.
Between them sit 5,434 stealer-log records tied to 1,500 distinct corporate email addresses, and 295 of the 482 surfaced in the last 90 days.
ChatGPT dominates the dataset; Hugging Face and Replit show developer tools are exposed as well
Break the dataset down by platform and one name swallows the chart. A captured ChatGPT or OpenAI session shows up for 358 of the 482 companies, and those companies carry roughly 90% of all records in the study. Zapier, Notion, Hugging Face, Replit, Lovable, and ElevenLabs trail far behind.
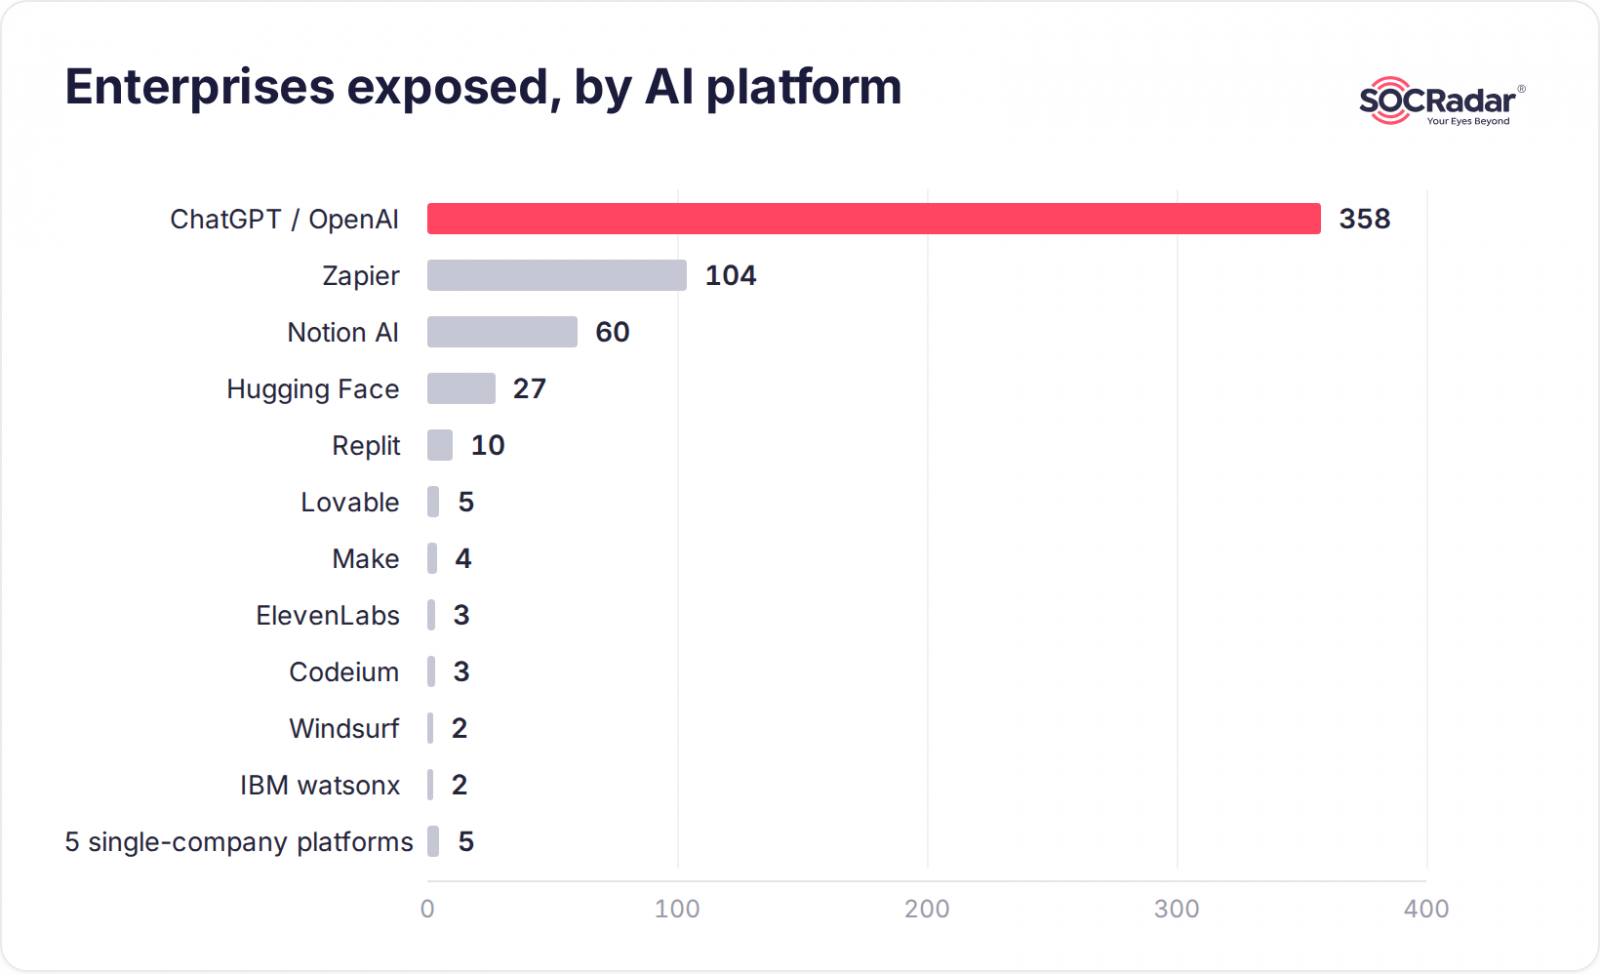
That skew matters, but the more interesting part is who is missing. There is no Claude in the top ranks. No Gemini.
|
Researcher comment
“We read ChatGPT’s near-total dominance as a shadow-AI signal, not a verdict on any vendor’s security. Its first-mover advantage means far more employees have quietly signed up with a work email on a personal device, and that is the population infostealers scrape. As adoption of other assistants catches up, we expect this chart to even out.”
|
It is a timely caveat. Anthropic’s own late-August incident showed Claude sessions are targeted the moment they exist in enough volume; the platform simply has a smaller corporate footprint to harvest today.
The lesson for a CISO is not “pick a safer assistant.” It is that the exposure follows the users, and the users are everywhere your policy isn’t.
Enter one work domain to see which AI platforms show stolen employee logins, how many records, and how recent.
Need no signup, updated daily across 44 AI platforms.
Why a stolen AI login is worse than a stolen password
A traditional credential unlocks one app. An AI account is four things at once: a searchable archive, an execution engine, a billable resource and an identity. A stolen session hands over all four without a password prompt.
The conversation history is the breach
Employees paste source code, customer records, contracts and unreleased plans into prompts. The account becomes a store of corporate memory, and whoever replays the session inherits that archive before touching an internal system.
Session cookies walk past MFA
A stolen cookie is a live session. As Okta’s Jeremy Kirk has put it, session tokens and API keys are sought out precisely because they can be replayed to bypass credential-based authentication. Rotating the password leaves the intruder signed in.
Agents act with the employee’s authority
Automation platforms hold standing OAuth grants into CRM, email and storage. A stolen Zapier session lets an attacker build a workflow that exfiltrates data on a schedule, from a vendor’s trusted IP space.
API keys are money, capacity and cover – LLMjacking
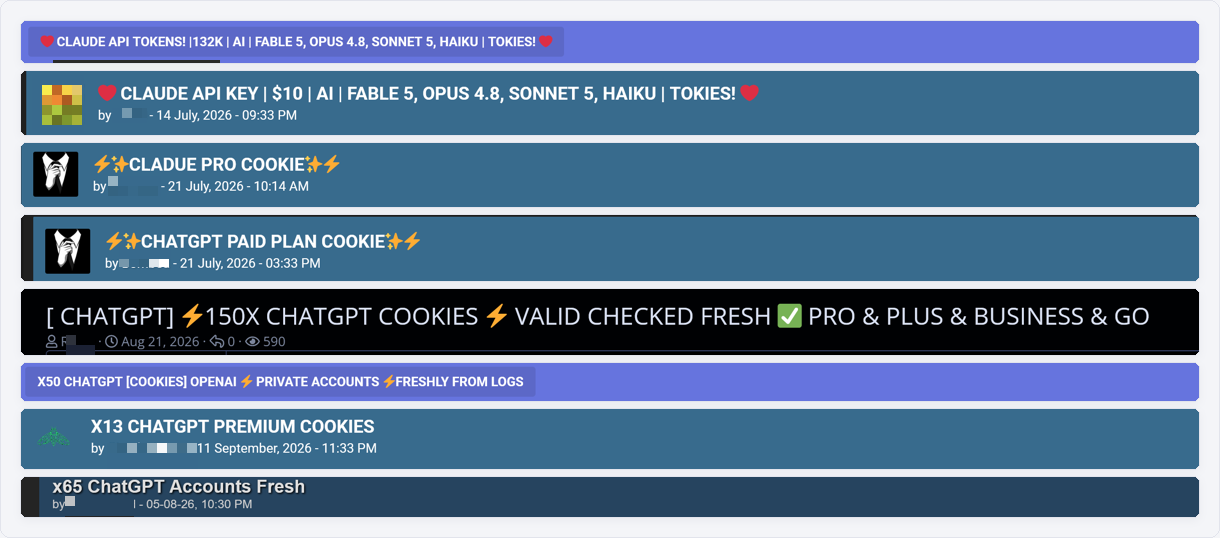
Keys copied into a notes app or a workspace settings page get lifted with everything else, then billed to the victim or resold. Underground vendors sell discounted access to Claude, Gemini and Cursor accounts and money-back guarantees.
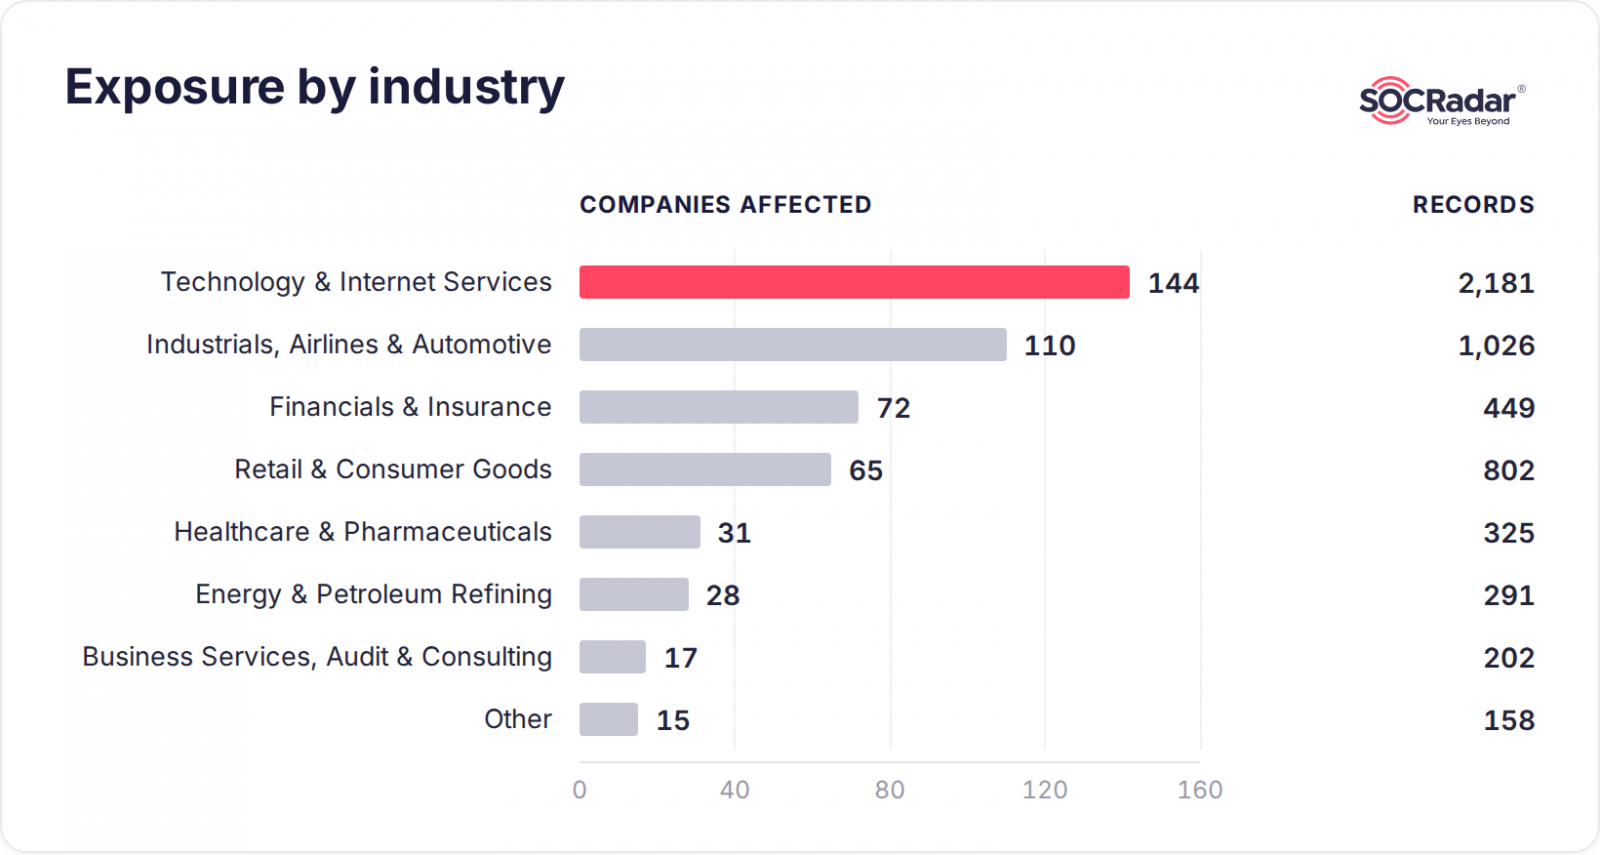
Technology leads, but the exposure is everywhere
Technology and internet-services firms are the single largest group at 144 companies and 40% of all records, and these firms hold data for many downstream clients.
Industrials, financial services, retail, healthcare, and energy all appear in force.
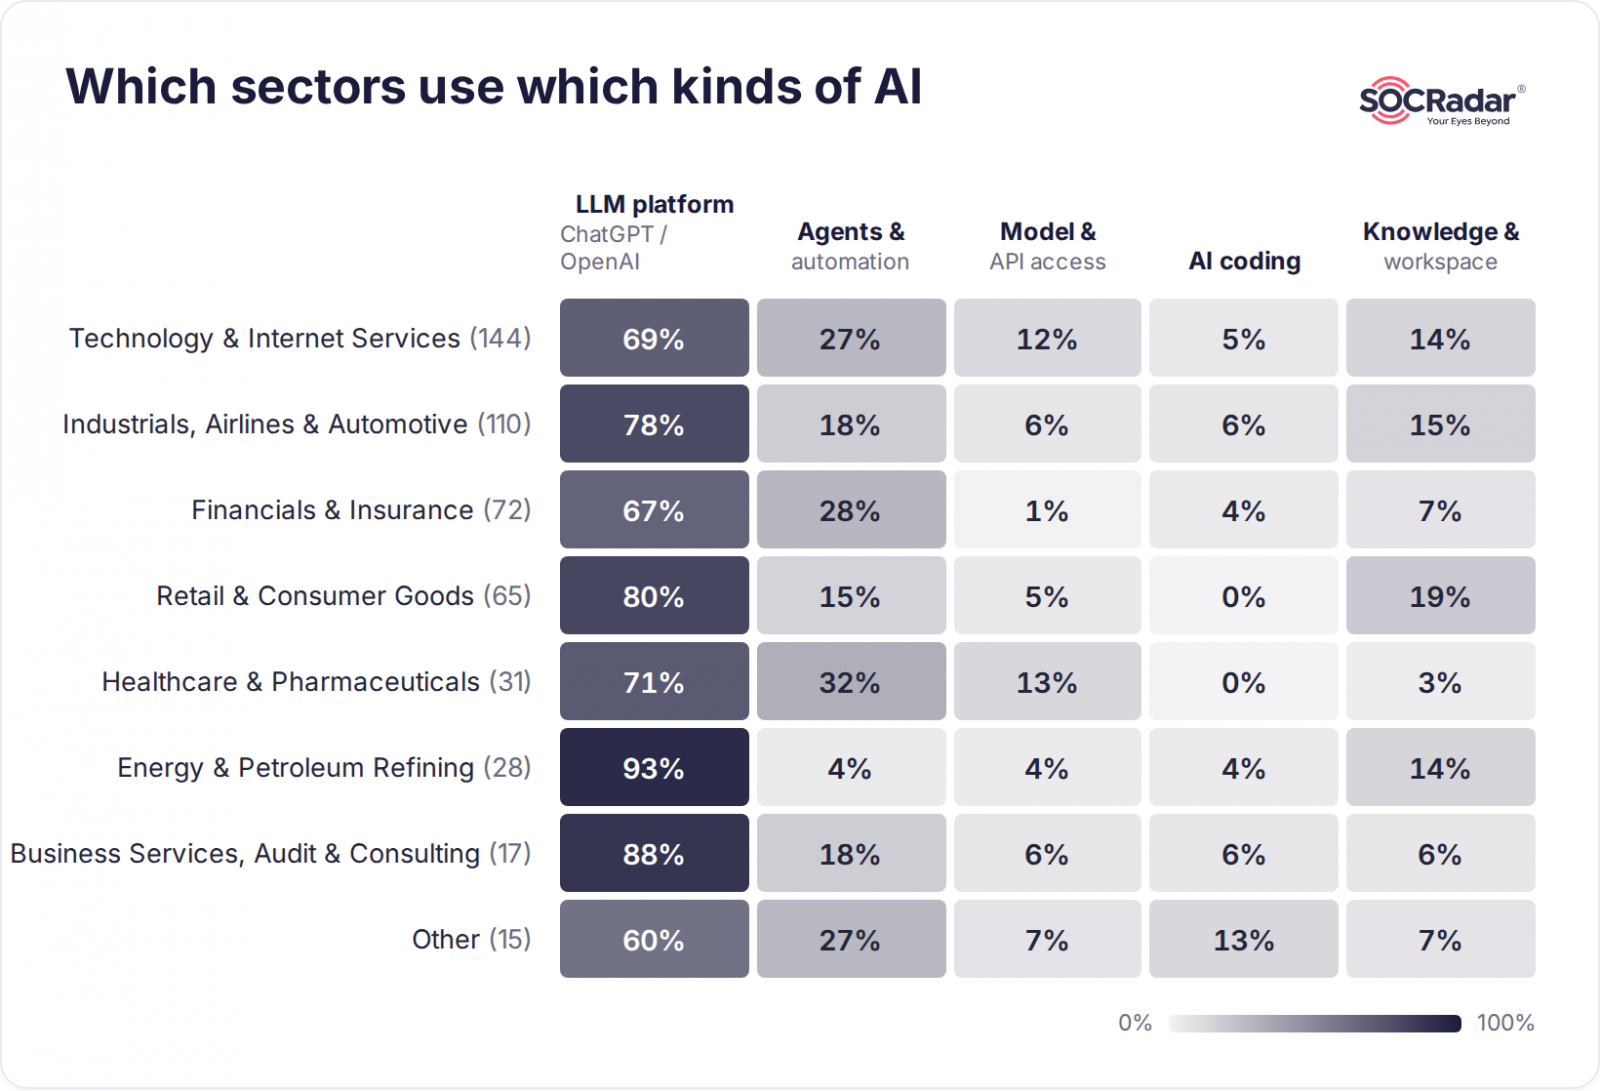
Break the same sectors down by what kind of AI is exposed and the risk profile shifts. LLM-platform exposure is near-universal, highest in energy at 93% of affected companies.
Agent and automation exposure, which carries an employee’s authority into other systems, concentrates in healthcare, financial services and technology.
None of this needs an autonomous agent swarm. One employee, one unmanaged laptop, one saved ChatGPT password and one commodity infostealer that has been on sale in Telegram channels since 2022 is enough.
What to do about it
The controls are not exotic. What is new is that AI platforms now belong in the same tier as your identity provider and your code repositories.
- Put every AI platform behind SSO with short-lived sessions: Use OAuth 2.0 / OIDC with refresh-token rotation so a stolen cookie expires before it can be sold. SSO removes the saved password, not the live session cookie, and does nothing for accounts opened before the policy existed.
- Scope, cap and rotate API keys: Alert on usage from unfamiliar ASNs or at odd hours – the fingerprint of LLMjacking.
- Monitor for session-token reuse: A session that changes country or device fingerprint mid-life is a replayed session. Treat any employee appearing in a stealer log as an endpoint incident, not a password reset.
- Find the shadow accounts first: You cannot rotate what you don’t know exists. Start by finding which of your domains already appear in stealer logs. You can use SOCRadar’s free AI Identity Exposure tool.
Bottom Line
Anthropic’s response to its own incident is the template worth copying: it invalidated sessions, stripped the payment methods attackers were abusing, and notified the people whose machines were infected before the fraud reached them.
See the complete report by SOCRadar.
Sponsored and written by SOCRadar.
