Close Menu

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Black Hat USA 2026 | Trusted Enough to Run: Breaking AI Agents in Official Workflows

    November 22, 2026

    Black Hat USA 2026 | Anatomy of a Takedown: Inside the Operation That Broke LockBit

    November 21, 2026

    DEF CON CTF Walkthrough: Web Exploitation

    November 20, 2026
    Facebook X (Twitter) Instagram
    • Demos
    • Technology
    • Gaming
    • Buy Now
    Facebook X (Twitter) Instagram Pinterest Vimeo
    Canadian Cyber WatchCanadian Cyber Watch
    • Home
    • News
    • Alerts
    • Tips
    • Tools
    • Industry
    • Incidents
    • Events
    • Education
    Subscribe
    Canadian Cyber WatchCanadian Cyber Watch
    Home»News»JadePuffer agentic AI attacks target Azure, destroy cloud resources
    News

    JadePuffer agentic AI attacks target Azure, destroy cloud resources

    adminBy adminSeptember 28, 2026No Comments3 Mins Read
    Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


    JadePuffer agentic AI attacks target Azure, destroy cloud resources

    The JadePuffer ransomware operator is targeting Azure tenants with agent-driven attacks that conduct reconnaissance, steal credentials, and destroy core components.

    The malware emerged in July, with researchers at cloud security company Sysdig highlighting that it uses AI agents to automate the entire attack chain, from reconnaissance, credential theft, and lateral movement to persistence and data encryption.

    Shortly after, the company noted that JadePuffer expanded its focus to AI assets, training datasets, and vector databases, using a tool called EncForge.

    Microsoft Security Research observed two JadePuffer attacks in June that mapped cloud resources, retrieved storage account keys, and deleted Azure Storage accounts.

    The destructive stage lasted seven minutes and targeted more than 100 storage accounts, as well as Key Vaults, Function Apps, Virtual Machines, and App Services.

    Although the threat actor was able to delete most of the targeted Azure Storage accounts, some remained unaffected because of Azure resource locks and storage account-level protections.

    Microsoft tracks the JadePuffer threat actor as Storm-3168 and says it used two compromised service principals – security identities that enable applications, hosted services, and automated tools to authenticate to Azure and access assigned resources.

    Both service principals belonged to the same tenant. One was used for reconnaissance and resource discovery, while the other “performed discovery, destructive operations, and credential collection.”
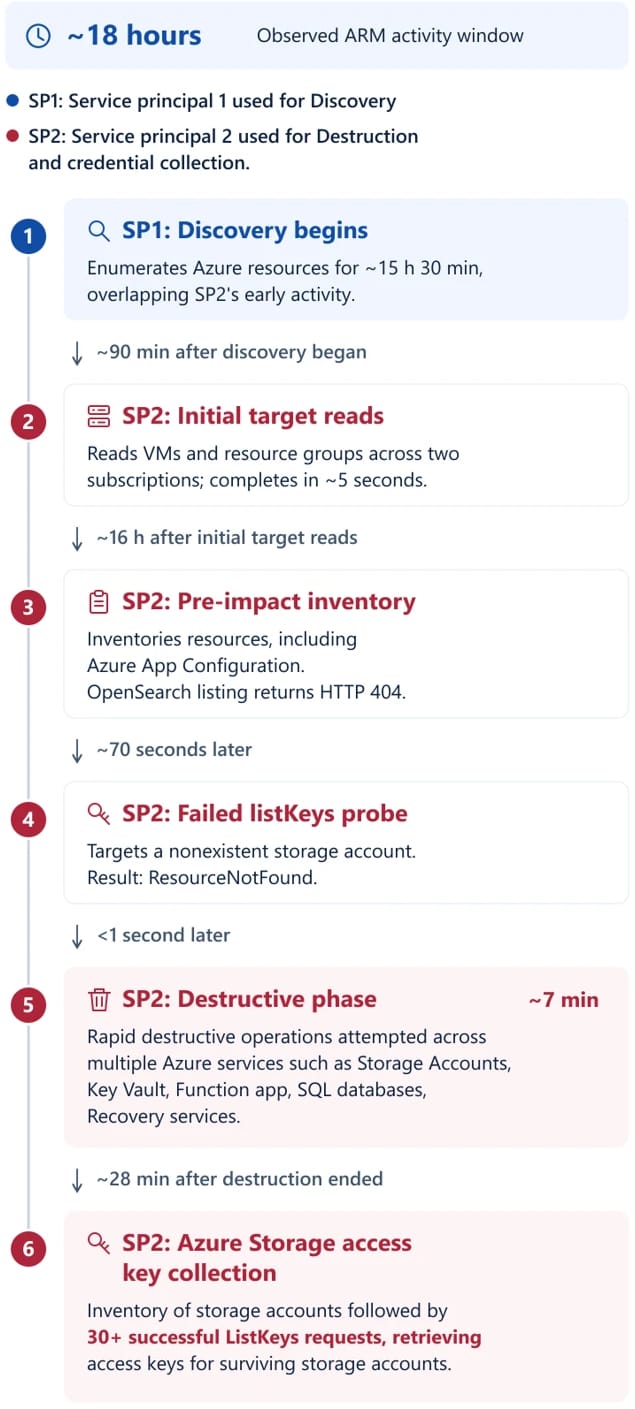
    Timeline of observed attacks
    Timeline of observed attacks
    Source: Microsoft

    The attacker removed backup and recovery protections (Azure Site Recovery locks), indicating an effort to make restoration more difficult.

    This operational pattern could further support ransomware extortion, although Microsoft did not report anything about financial demands and didn’t confirm data theft in the observed cases.

    According to the researchers, attempts to delete Azure SQL databases failed because the attacker used an unsupported API version. Attempts to remove recovery protection locks also failed.

    “The parallel targeting of Azure SQL databases and storage accounts suggests an effort to broaden the destructive impact across different data services rather than concentrating on a single resource type,” Microsoft said.

    Roughly half an hour after the wipe attempts, Storm-3168 returned to perform more than 30 requests for storage account keys, most of which succeeded.

    Microsoft could not determine exactly how the initial access occurred, but noted that credentials for one service principal appeared in a public GitHub issue before the attacks.

    The researchers recommend several mitigation steps and guidance for system administrators, including activating cloud workload protections, checking for secrets in public repositories, and evaluating Azure RBAC permissions against least-privilege principles.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat


    Source link

    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    Previous ArticleDutch police confirm arrest in ShinyHunters hacking investigation
    Next Article 80,000+ Organizations Had AI Logins Stolen: From Shadow AI to LLMjacking
    admin
    • Website

    Related Posts

    News

    JCTables for Joomla: When “Already Escaped” Means Injectable | Blog

    October 1, 2026
    News

    Vulnerability Discovery and Exploitation Trends in the AI Era

    October 1, 2026
    News

    Microsoft is rolling out Linux container support to WSL

    September 30, 2026
    Add A Comment

    Comments are closed.

    Demo
    Top Posts

    Catchy & Intriguing

    March 17, 202684 Views

    How to prove false statements? (Part 3)

    March 24, 202668 Views

    The Package That Never Was: How Delivery Service Scams Are Fooling Canadians

    April 1, 202665 Views
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram
    Latest Reviews
    85
    Featured

    Pico 4 Review: Should You Actually Buy One Instead Of Quest 2?

    January 15, 2021 Featured
    8.1
    Uncategorized

    A Review of the Venus Optics Argus 18mm f/0.95 MFT APO Lens

    January 15, 2021 Uncategorized
    8.9
    Editor's Picks

    DJI Avata Review: Immersive FPV Flying For Drone Enthusiasts

    January 15, 2021 Editor's Picks

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Demo
    Most Popular

    Catchy & Intriguing

    March 17, 202684 Views

    How to prove false statements? (Part 3)

    March 24, 202668 Views

    The Package That Never Was: How Delivery Service Scams Are Fooling Canadians

    April 1, 202665 Views
    Our Picks

    Black Hat USA 2026 | Trusted Enough to Run: Breaking AI Agents in Official Workflows

    November 22, 2026

    Black Hat USA 2026 | Anatomy of a Takedown: Inside the Operation That Broke LockBit

    November 21, 2026

    DEF CON CTF Walkthrough: Web Exploitation

    November 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook X (Twitter) Instagram Pinterest
    • Home
    • Technology
    • Gaming
    • Phones
    • Buy Now
    © 2026 ThemeSphere. Designed by ThemeSphere.

    Type above and press Enter to search. Press Esc to cancel.