Close Menu

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Black Hat USA 2026 | Anatomy of a Takedown: Inside the Operation That Broke LockBit

    November 21, 2026

    DEF CON CTF Walkthrough: Web Exploitation

    November 20, 2026

    Minecraft Malware Lab

    November 19, 2026
    Facebook X (Twitter) Instagram
    • Demos
    • Technology
    • Gaming
    • Buy Now
    Facebook X (Twitter) Instagram Pinterest Vimeo
    Canadian Cyber WatchCanadian Cyber Watch
    • Home
    • News
    • Alerts
    • Tips
    • Tools
    • Industry
    • Incidents
    • Events
    • Education
    Subscribe
    Canadian Cyber WatchCanadian Cyber Watch
    Home»News»GitHub Actions re-enabled with Mini Shai-Hulud payload still active
    News

    GitHub Actions re-enabled with Mini Shai-Hulud payload still active

    adminBy adminSeptember 26, 2026No Comments3 Mins Read
    Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


    GitHub Actions re-enabled with Mini Shai-Hulud payload still active

    Two third-party GitHub Actions previously compromised in a Mini Shai-Hulud campaign were re-enabled by their maintainer and remained accessible for more than a week despite still pointing to malicious code.

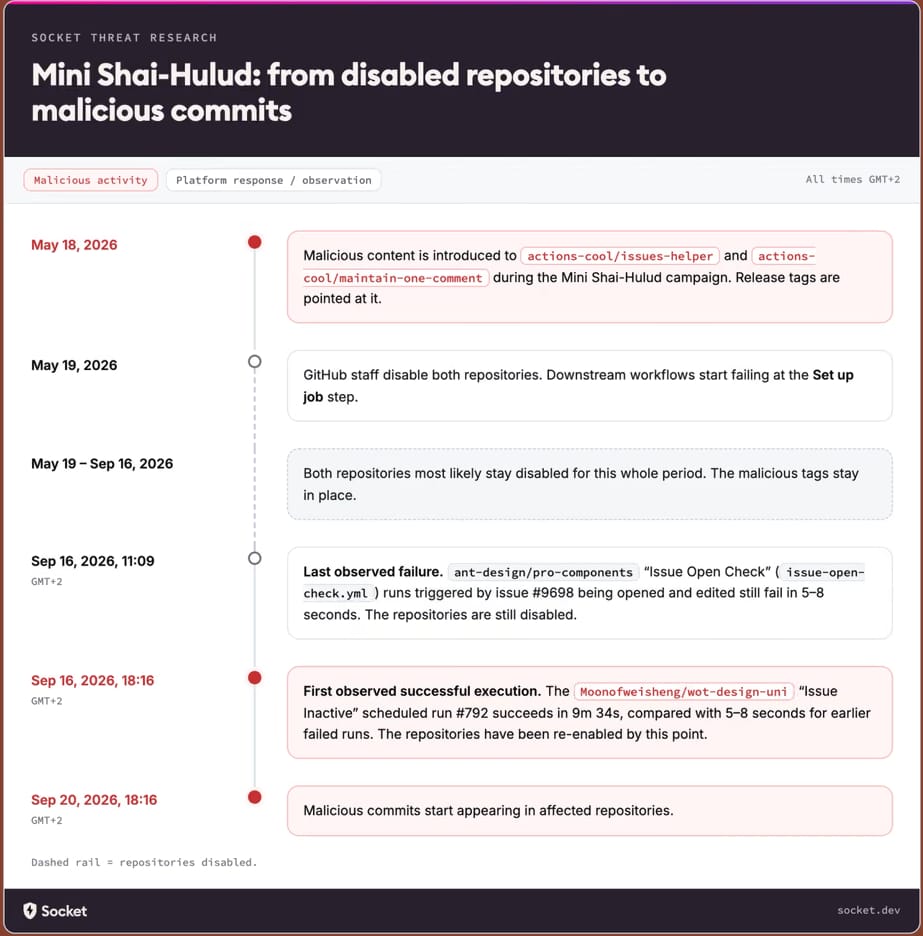
    After being compromised on May 18, the GitHub security team removed actions-cool/issues-helper and actions-cool/maintain-one-comment, preventing any downstream workflow from downloading malware.

    According to researchers at application security company Socket, starting September 16 and up to September 25, the two actions became active again with the same release tags, causing workflows referencing their actions to download and execute the old payload.

    The Mini Shai-Hulud supply-chain attack in May affected 323 packages and 639 package versions on the Node Package Manager (npm) index, infecting them with malware that targets developers’ tokens, credentials, and CI/CD secrets.

    Socket researchers found that last Wednesday the release tags for actions-cool/issues-helper and actions-cool/maintain-one-comment resolved to a commit containing the obfuscated payload inside the ‘index.js’ file.

    “On September 16, 2026, both repositories became accessible again. Their release tags were not cleaned up first,” Socket explained.

    “They still point to the malicious content introduced on May 18, so any workflow that references either action by a version tag resumed downloading and executing the payload on its next run.”

    It is unclear exactly why these repositories were re-enabled without proper cleaning occurring first.
    Incident timeline
    Incident timeline
    Source: Socket

    Socket says that GitHub’s dependency graph lists about 15,000 repositories depending on ‘issues-helper,’ though this does not mean all of them were compromised.

    The researchers note that they have not yet established how many dependents reference either action by mutable tag instead of a pinned commit.

    However, they explained that the impacted actions are those running almost daily, as they support issue-housekeeping needs.

    On September 25, Socket found that both actions were disabled again on GitHub, leading workflows that reference them to fail instead of running the payload.

    Socket recommends finding references to both actions, removing them or pinning a verified clean commit, reviewing runs since September 16, and rotating secrets accessible to workflows that ran an affected tag.

    Potentially impacted developers should look for references to both actions and remove them or pin a verified clean commit.

    The exposure started on September 16 between 11:09 and 18:16 GMT+2.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat


    Source link

    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    Previous ArticleCISA warns of Sharepoint, WSO2, Adobe Commerce flaws exploited in attacks
    Next Article Departmental Activity Review of the Canadian Security Intelligence Service
    admin
    • Website

    Related Posts

    News

    JCTables for Joomla: When “Already Escaped” Means Injectable | Blog

    October 1, 2026
    News

    Vulnerability Discovery and Exploitation Trends in the AI Era

    October 1, 2026
    News

    Microsoft is rolling out Linux container support to WSL

    September 30, 2026
    Add A Comment

    Comments are closed.

    Demo
    Top Posts

    Catchy & Intriguing

    March 17, 202684 Views

    How to prove false statements? (Part 3)

    March 24, 202666 Views

    The Package That Never Was: How Delivery Service Scams Are Fooling Canadians

    April 1, 202665 Views
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram
    Latest Reviews
    85
    Featured

    Pico 4 Review: Should You Actually Buy One Instead Of Quest 2?

    January 15, 2021 Featured
    8.1
    Uncategorized

    A Review of the Venus Optics Argus 18mm f/0.95 MFT APO Lens

    January 15, 2021 Uncategorized
    8.9
    Editor's Picks

    DJI Avata Review: Immersive FPV Flying For Drone Enthusiasts

    January 15, 2021 Editor's Picks

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Demo
    Most Popular

    Catchy & Intriguing

    March 17, 202684 Views

    How to prove false statements? (Part 3)

    March 24, 202666 Views

    The Package That Never Was: How Delivery Service Scams Are Fooling Canadians

    April 1, 202665 Views
    Our Picks

    Black Hat USA 2026 | Anatomy of a Takedown: Inside the Operation That Broke LockBit

    November 21, 2026

    DEF CON CTF Walkthrough: Web Exploitation

    November 20, 2026

    Minecraft Malware Lab

    November 19, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook X (Twitter) Instagram Pinterest
    • Home
    • Technology
    • Gaming
    • Phones
    • Buy Now
    © 2026 ThemeSphere. Designed by ThemeSphere.

    Type above and press Enter to search. Press Esc to cancel.