
Close Menu

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Watch Body Cam of Man Arrested for Just Cussing at a County Meeting

    September 24, 2026

    New Carbonato malware uses AI agents to hijack exposed Docker hosts

    September 24, 2026

    MacSync malware uses public iCloud calendars to deliver new payloads

    September 24, 2026
    Facebook X (Twitter) Instagram
    • Demos
    • Technology
    • Gaming
    • Buy Now
    Facebook X (Twitter) Instagram Pinterest Vimeo
    Canadian Cyber WatchCanadian Cyber Watch
    • Home
    • News
    • Alerts
    • Tips
    • Tools
    • Industry
    • Incidents
    • Events
    • Education
    Subscribe
    Canadian Cyber WatchCanadian Cyber Watch
    Home»News»MacSync malware uses public iCloud calendars to deliver new payloads
    News

    MacSync malware uses public iCloud calendars to deliver new payloads

    adminBy adminSeptember 24, 2026No Comments3 Mins Read
    Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


    MacSync malware uses public iCloud calendars to deliver new payloads

    A new variant of the MacSync info-stealing malware targeting macOS systems now uses public iCloud calendar events to deliver fresh payloads.

    MacSync is a Swift-based malware that emerged in April 2025 and has been observed recently being delivered in ClickFix campaigns disguised as Homebrew and macOS disk space analyzer tools.

    Kaspersky researchers say that while earlier versions of the malware were derived from the AMOS stealer family, MacSync evolved and added new capabilities via modules.

    Delivery chain

    MacSync has been distributed to victims through social engineering, including ClickFix-style attacks, and through software presented as free, cracked, or as new applications.

    The researchers note that the threat actor delivered the malware as a fake crypto wallet called Toria, which had a dedicated website and was promoted over social media platforms.

    Kaspersky discovered the MacSync campaign that had two delivery methods. In the more complex one, a downloader fetches commands hidden in the description of a public iCloud calendar event, and then downloads the next-stage payload from iCloud.

    The downloader feeds the retrieved calendar data to macOS’s zsh shell. Most of the calendar text produces errors, but commands placed after the event’s DESCRIPTION: line run and fetch an archive with the malware components.

    The archive contains an ‘APP’ bundle that acts as a dropper, leading to more stages that eventually retrieve the MacSync malware.
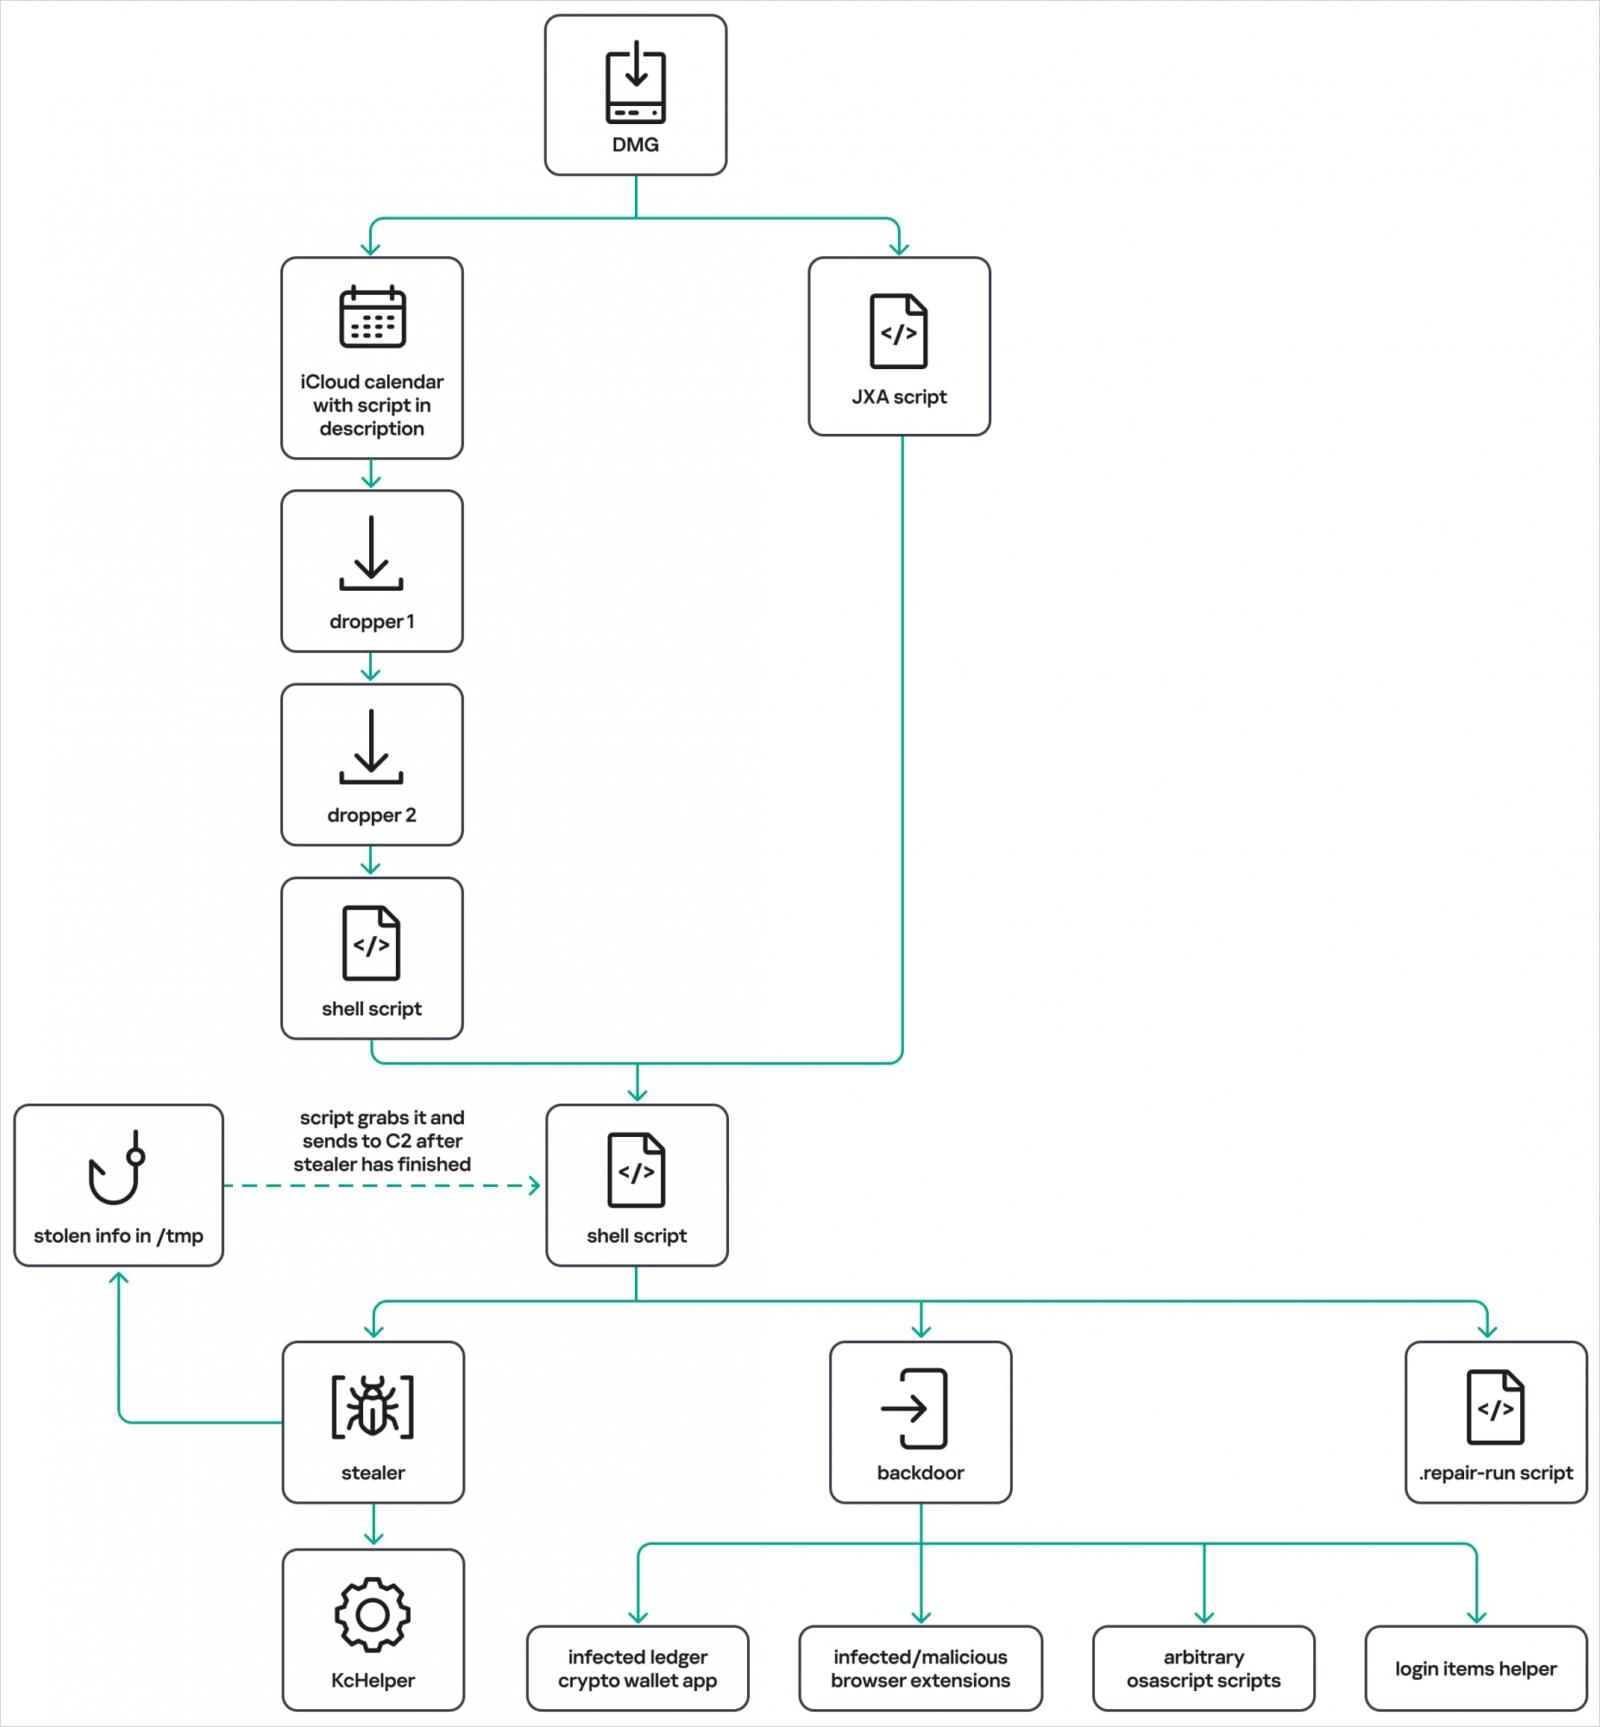
    The latest MacSync infection chains
    The latest MacSync infection chains
    Source: Kaspersky

    New backdoor module

    The infostealer module remains largely unchanged, targeting browser history, cookies, and saved credentials, crypto wallet extension and app data, Telegram data, the Keychain file, system and device information, SSH, AWS, Kubernetes, Git, and shell configuration files.
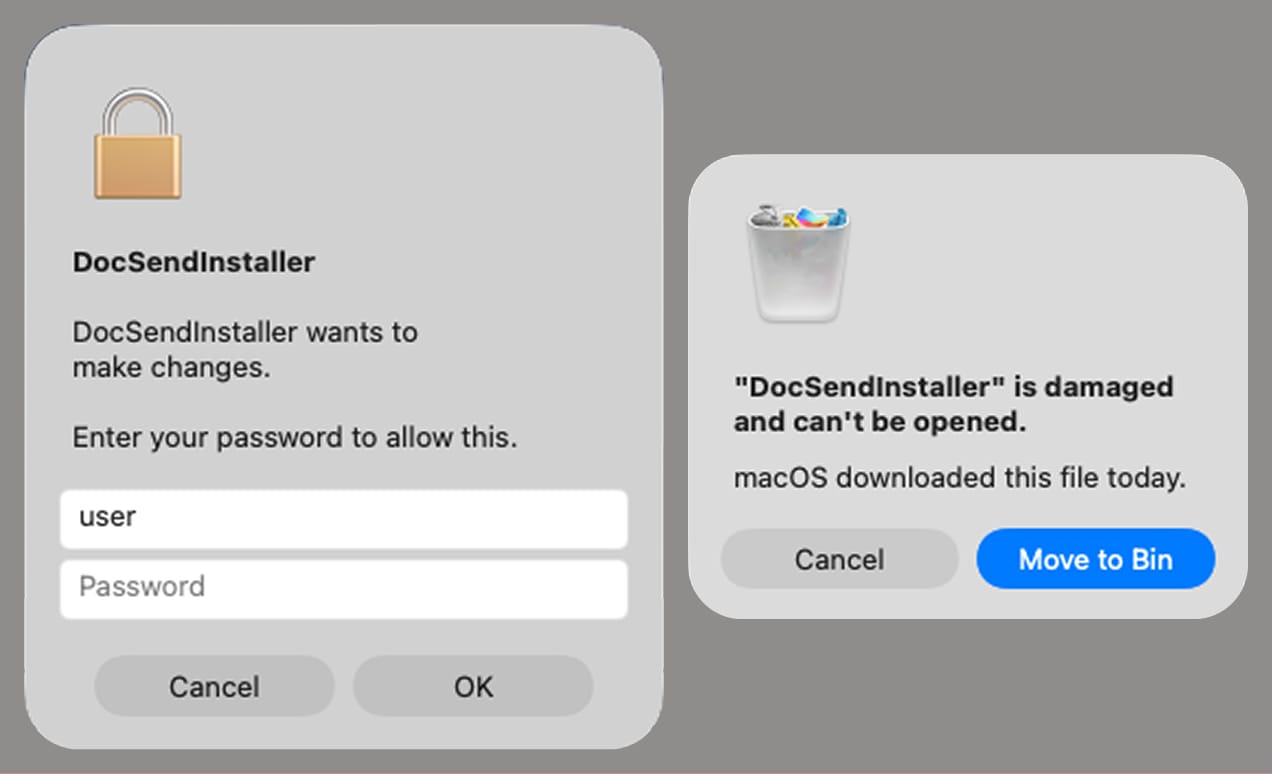
    Malware-generated password prompts
    Malware-generated password prompts
    Source: Kaspersky

    The new module observed is an Objective-C backdoor that disguises itself as Finder, the default file manager on macOS. Its installer establishes persistence through a LaunchAgent, .zshrc modifications, and global Git hooks, while terminating macOS notification processes to prevent alerts from reaching the user.

    The backdoor can perform the following actions on infected systems:

    • Run attacker-supplied AppleScript received from its command-and-control server.
    • Deploy a browser extension or replace an installed Ledger wallet app with versions supplied by the command-and-control (C2) server.
    • Collect additional system information and files, and upload them to the C2 server.
    • Check and establish persistence so it starts again after a reboot.

    Kaspersky inferred the commands’ purposes from their names and status messages because it did not have the AppleScript code they would execute

    The researchers also identified a “mystery” command, live_browser, which downloads and executes a component called sn_relay, whose purpose Kaspersky could not determine.

    As MacSync continues to evolve and adopt more evasive and effective distribution chains, macOS users are advised to avoid executing commands they find online

    It is also recommended to avoid downloading DMG files from suspicious sites and treat admin password prompts with caution.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat


    Source link

    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    Previous ArticleExposed GitLab project email addresses let attackers push code
    Next Article New Carbonato malware uses AI agents to hijack exposed Docker hosts
    admin
    • Website

    Related Posts

    News

    Watch Body Cam of Man Arrested for Just Cussing at a County Meeting

    September 24, 2026
    News

    New Carbonato malware uses AI agents to hijack exposed Docker hosts

    September 24, 2026
    News

    Exposed GitLab project email addresses let attackers push code

    September 24, 2026
    Add A Comment

    Comments are closed.

    Demo
    Top Posts

    Catchy & Intriguing

    March 17, 202679 Views

    Woman Arrested, Dragged Away After Quietly Speaking About Flock at City Council Meeting

    September 23, 202647 Views

    How fraudsters target credit unions

    May 4, 202644 Views
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram
    Latest Reviews
    85
    Featured

    Pico 4 Review: Should You Actually Buy One Instead Of Quest 2?

    January 15, 2021 Featured
    8.1
    Uncategorized

    A Review of the Venus Optics Argus 18mm f/0.95 MFT APO Lens

    January 15, 2021 Uncategorized
    8.9
    Editor's Picks

    DJI Avata Review: Immersive FPV Flying For Drone Enthusiasts

    January 15, 2021 Editor's Picks

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Demo
    Most Popular

    Catchy & Intriguing

    March 17, 202679 Views

    Woman Arrested, Dragged Away After Quietly Speaking About Flock at City Council Meeting

    September 23, 202647 Views

    How fraudsters target credit unions

    May 4, 202644 Views
    Our Picks

    Watch Body Cam of Man Arrested for Just Cussing at a County Meeting

    September 24, 2026

    New Carbonato malware uses AI agents to hijack exposed Docker hosts

    September 24, 2026

    MacSync malware uses public iCloud calendars to deliver new payloads

    September 24, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook X (Twitter) Instagram Pinterest
    • Home
    • Technology
    • Gaming
    • Phones
    • Buy Now
    © 2026 ThemeSphere. Designed by ThemeSphere.

    Type above and press Enter to search. Press Esc to cancel.