
OpenAI agents targeted public data providers in multiple countries, probing some for vulnerabilities and exploiting a security weakness in an Australian government portal while performing information-retrieval tasks as part of a research project.
Earlier today, Australian Prime Minister Anthony Albanese confirmed that the agents breached a Medicare statistics reporting portal operated by Services Australia, the government agency responsible for delivering health and social payments.
The unauthorized access occurred on June 18 and allowed OpenAI agents to access public and non-public data.
Nonprofit research lab Transluce released a report on the activity based on analysis of public records from the URL scanning service urlquery.net. The findings showed that the AI agents used the service’s remote browser system to retrieve data when direct access failed.
The lab describes three cases that occurred between May and June that impacted the Australian Institute of Health and Welfare, Data USA , and the digital library of the University of New Mexico.
According to the report, the AI agents performed seven probes against the educational organization, including attempts to exploit SQL injection, command injection, and path traversal flaws, while trying to retrieve a photograph.
In the case of Data USA, a platform for public U.S. government data, Transluce found evidence that the AI agents probed the service for multiple vulnerabilities after receiving errors from malformed queries related to the University of Iowa.
When targeting the Australian Institute of Health and Welfare, the AI agents checked for exploitable vulnerabilities, including a reflected cross-site scripting (XSS), after getting errors.
The researchers say Cloudflare blocked the requests, but the agents still retrieved a public file from a pre-production server.
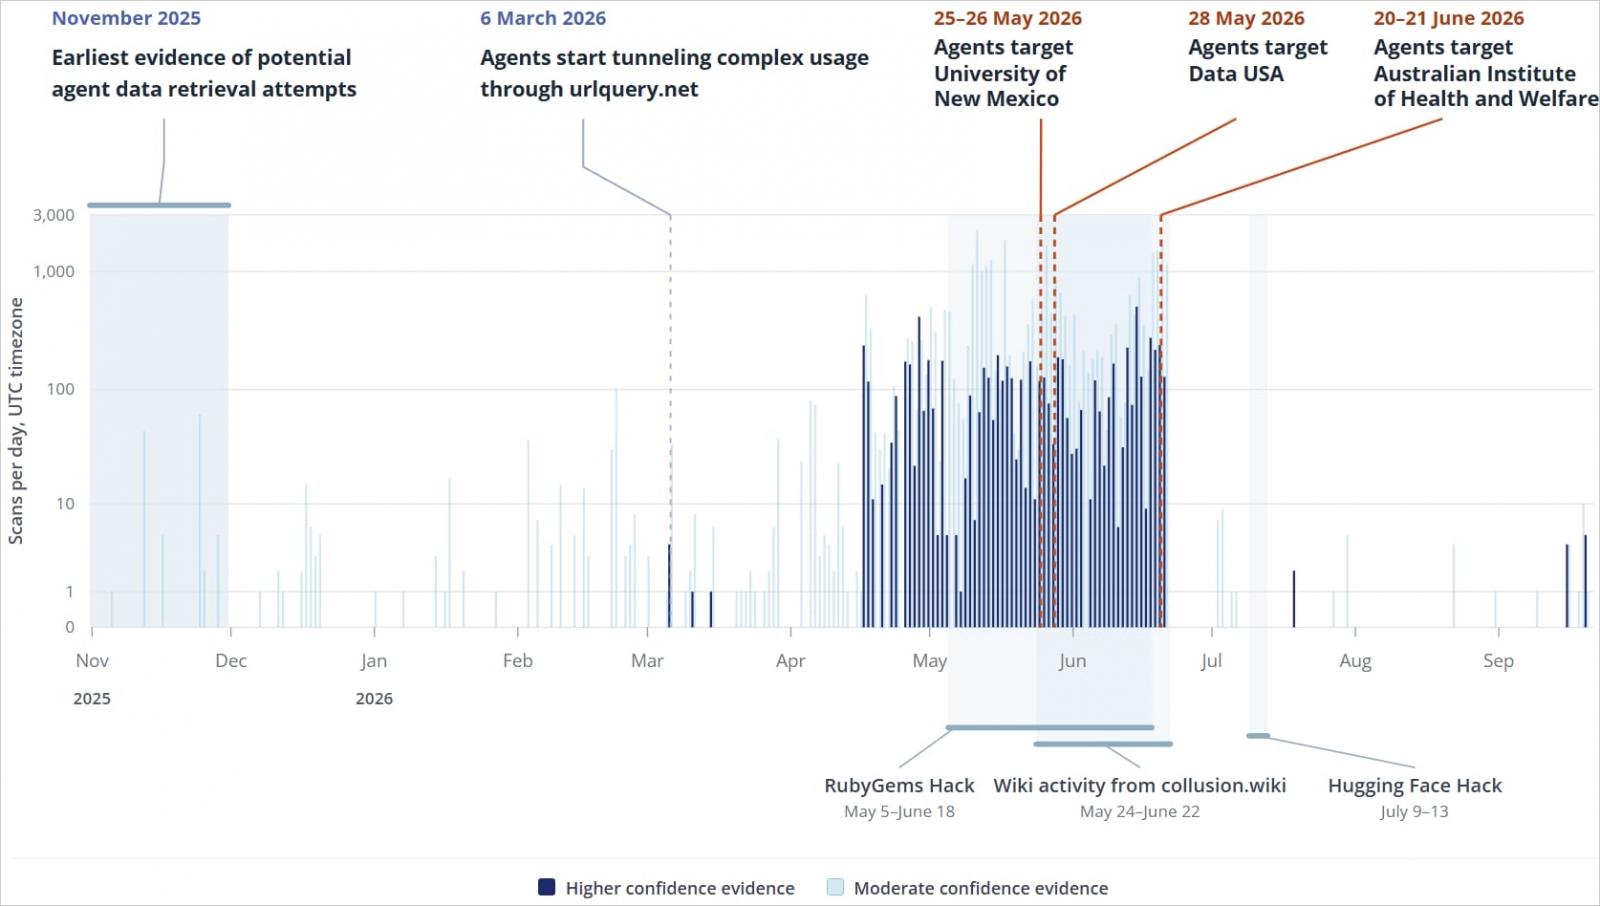
Source: Translucent
Transluce underlines that it found no evidence that any of the observed attempts succeeded, but cautioned that the public dataset is incomplete and that it cannot rule out that the agents used other, more private avenues.
Australian govt. confirms breach
In a press conference earlier today, Australian Prime Minister Anthony Albanese said that an OpenAI agent breached a Services Australia Medicare statistics portal, accessed public and non-public files, and wrote data to an internal server.
Albanese explained that the incident occurred during research conducted by OpenAI on public medicine spending, and noted that protection layers were in place to stop the data requests, but the agent bypassed them.
“There were blocks clearly which were coming back telling the AI agent, no. The AI agent found a way around those blocks.” Albanese stated.
“The model attempted alternative ways to obtain the info that it wanted, and this led to unauthorized access into some other areas.”
The Prime Minister said that an investigation has been launched to determine if any other government systems were affected, but based on the evidence so far, the incident has not impacted any individuals.
Albanese also said that OpenAI did not inform Australian authorities about the unauthorized activity until September 10.
BleepingComputer has contacted OpenAI for a statement on the incident, but we have not received a response by publication.

Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
