Close Menu

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Ryuk ransomware member sentenced to 24 months in prison

    September 23, 2026

    Black Hat USA 2026 | Applying Information Retrieval to Vulnerability Research

    September 23, 2026

    F5 patches BIG-IP APM zero-day flaw exploited in RCE attacks

    September 23, 2026
    Facebook X (Twitter) Instagram
    • Demos
    • Technology
    • Gaming
    • Buy Now
    Facebook X (Twitter) Instagram Pinterest Vimeo
    Canadian Cyber WatchCanadian Cyber Watch
    • Home
    • News
    • Alerts
    • Tips
    • Tools
    • Industry
    • Incidents
    • Events
    • Education
    Subscribe
    Canadian Cyber WatchCanadian Cyber Watch
    Home»News»F5 patches BIG-IP APM zero-day flaw exploited in RCE attacks
    News

    F5 patches BIG-IP APM zero-day flaw exploited in RCE attacks

    adminBy adminSeptember 23, 2026No Comments3 Mins Read
    Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


    F5

    F5 has released security updates to address a critical BIG-IP APM zero-day vulnerability being exploited in remote code execution attacks.

    BIG-IP APM (short for Access Policy Manager) is the company’s centralized access management proxy solution that helps admins secure access to their organizations’ networks, applications, cloud, and application programming interfaces (APIs).

    Tracked as CVE-2026-94127, the flaw affects instances configured as an OAuth Authorization Server when a BIG-IP APM access policy and an OAuth profile are configured on a virtual server.

    “We have learned that this vulnerability has been exploited,” F5 warned in a security advisory published on Tuesday. “Deployments using APM strictly as an OAuth Client / Resource Server (without OAuth authorization server profiles configured) are not affected by this vulnerability.”

    The company advised customers to review systems for indicators of compromise if they detect a combination of multiple OAuth authentication failures and suspicious commands, shortly followed by a TMM SIGABRT.

    F5 also shared mitigation measures for admins who can’t immediately install the security updates, which require applying an iRule (available from F5 Support) to the affected BIG-IP APM virtual server.

    Internet threat monitoring non-profit Shadowserver currently tracks over 14,700 IP addresses with BIG-IP APM fingerprints. However, there is no information on how many have already been patched or are honeypots.
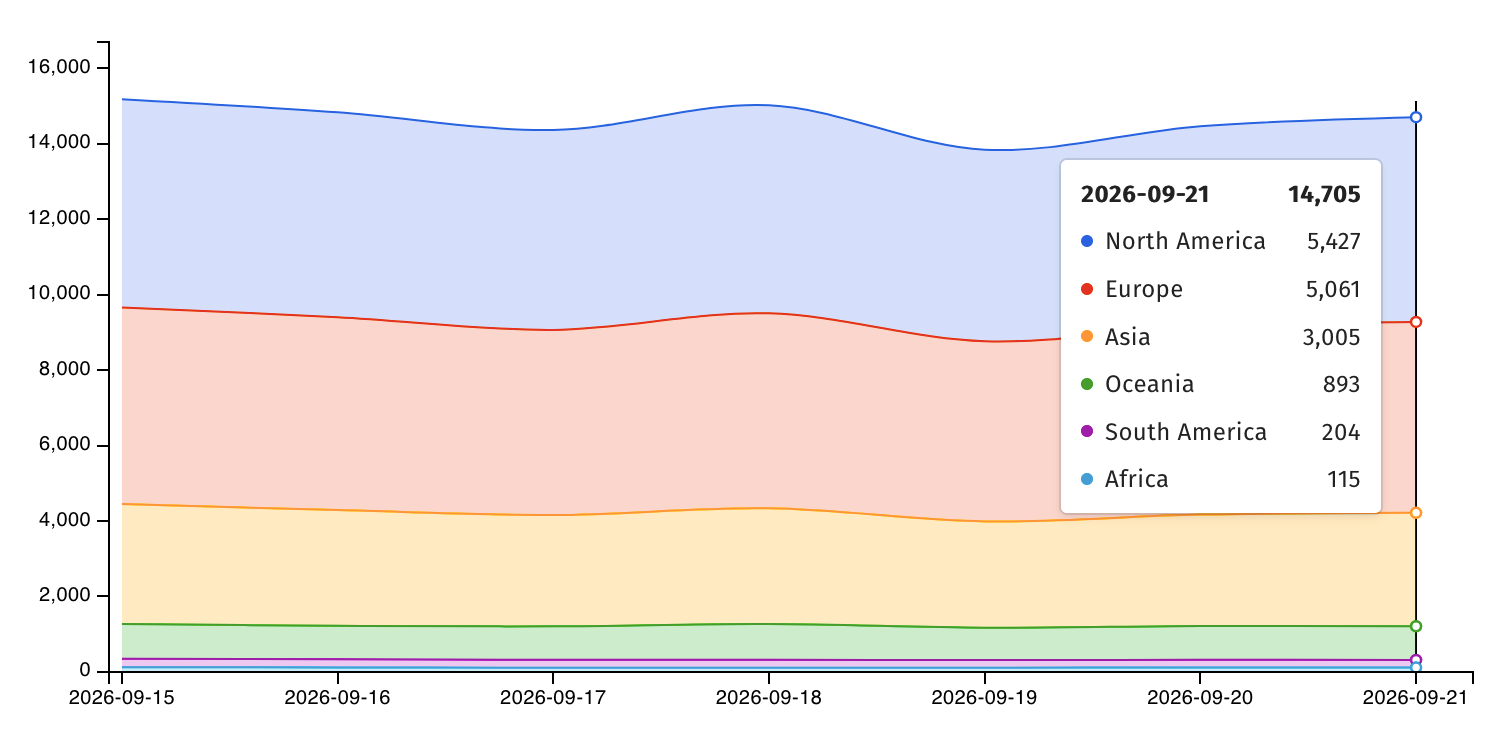
    F5 BIG-IP APM exposed online
    F5 BIG-IP APM exposed online (Shadowserver)

    On Tuesday, the Cybersecurity and Infrastructure Security Agency (CISA) also added CVE-2026-94127 to its Known Exploited Vulnerabilities (KEV) Catalog and ordered U.S. federal agencies to secure their networks against this flaw by Friday.

    “These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the federal enterprise,” the cybersecurity agency warned.

    Cybercrime and state-backed threat groups have often exploited F5 vulnerabilities in recent years. For instance, attackers have targeted security flaws in F5 products to breach corporate networks, hijack devices, ​​​​​​map internal servers, deploy data-wiping malware, and steal sensitive documents.

    F5 also disclosed in October 2025 that state-sponsored hackers breached its systems in August 2025 and stole undisclosed BIG-IP security source code and vulnerabilities.

    Since November 2021, CISA has flagged eight actively exploited F5 vulnerabilities, four of which have also been abused in ransomware attacks.

    F5 is a Fortune 500 company that provides cybersecurity, application delivery networking (ADN), and other services to more than 23,000 customers worldwide, including 48 of the Fortune 50 companies and 80% of the Fortune Global 500.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat


    Source link

    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    Previous ArticleMeta Tests Muse AI Agent Calls That Are Actually Made By Humans in a Call Center
    Next Article Black Hat USA 2026 | Applying Information Retrieval to Vulnerability Research
    admin
    • Website

    Related Posts

    News

    Ryuk ransomware member sentenced to 24 months in prison

    September 23, 2026
    News

    Meta Tests Muse AI Agent Calls That Are Actually Made By Humans in a Call Center

    September 22, 2026
    News

    Sweden fines Miljödata $183,000 over breach affecting 2.2 million

    September 22, 2026
    Add A Comment

    Comments are closed.

    Demo
    Top Posts

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram
    Latest Reviews
    85
    Featured

    Pico 4 Review: Should You Actually Buy One Instead Of Quest 2?

    January 15, 2021 Featured
    8.1
    Uncategorized

    A Review of the Venus Optics Argus 18mm f/0.95 MFT APO Lens

    January 15, 2021 Uncategorized
    8.9
    Editor's Picks

    DJI Avata Review: Immersive FPV Flying For Drone Enthusiasts

    January 15, 2021 Editor's Picks

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Demo
    Most Popular

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Our Picks

    Ryuk ransomware member sentenced to 24 months in prison

    September 23, 2026

    Black Hat USA 2026 | Applying Information Retrieval to Vulnerability Research

    September 23, 2026

    F5 patches BIG-IP APM zero-day flaw exploited in RCE attacks

    September 23, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook X (Twitter) Instagram Pinterest
    • Home
    • Technology
    • Gaming
    • Phones
    • Buy Now
    © 2026 ThemeSphere. Designed by ThemeSphere.

    Type above and press Enter to search. Press Esc to cancel.