

Close Menu

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Malicious npm packages evade install-script defenses at runtime

    September 20, 2026

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026

    Microsoft Teams will let admins block custom file extensions

    September 20, 2026
    Facebook X (Twitter) Instagram
    • Demos
    • Technology
    • Gaming
    • Buy Now
    Facebook X (Twitter) Instagram Pinterest Vimeo
    Canadian Cyber WatchCanadian Cyber Watch
    • Home
    • News
    • Alerts
    • Tips
    • Tools
    • Industry
    • Incidents
    • Events
    • Education
    Subscribe
    Canadian Cyber WatchCanadian Cyber Watch
    Home»News»Chinese hackers use SparroWocky malware in govt espionage attacks
    News

    Chinese hackers use SparroWocky malware in govt espionage attacks

    adminBy adminSeptember 17, 2026No Comments3 Mins Read
    Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


    Chinese hackers use SparroWocky malware in govt espionage attacks

    The China-linked espionage group FamousSparrow has been using a new backdoor named SparroWocky in attacks on government organizations in Latin America.

    The operations have been ongoing for more than a year, with the new malware replacing the previously used SparrowDoor custom backdoor.

    ESET researchers observed SparroWocky in attacks targeting organizations in Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela.

    The researchers believe the threat actor’s objective was to collect intelligence on Latin American governments’ responses to increasing U.S. pressure on Chinese economic interests.
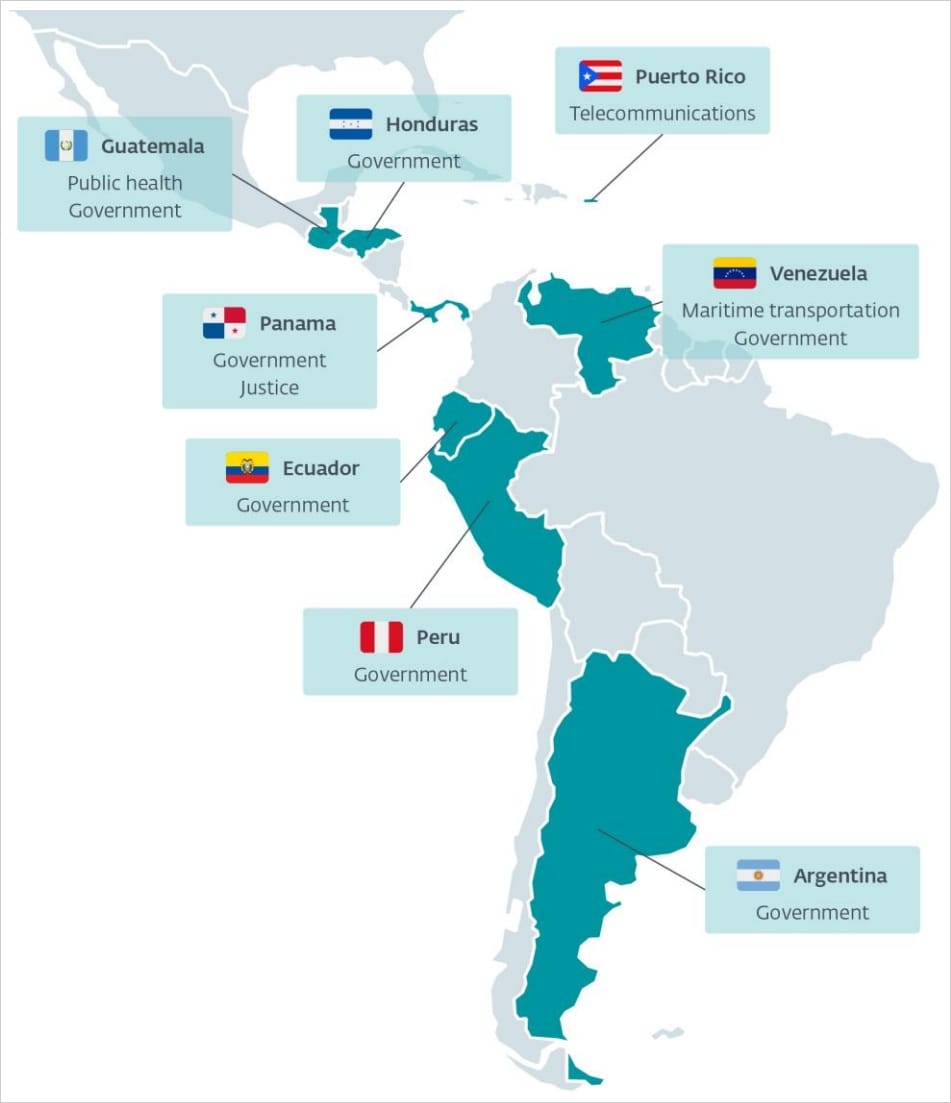
    FamousSparrow victims
    FamousSparrow victims
    Source: ESET

    ESET’s analysis revealed that SparroWocky is a modular, full-blown C++ backdoor that includes code from open-source projects.

    The malware features anti-analysis mechanisms, like manipulating low-level structures in memory and patching code at runtime. SparroWocky’s capabilities include:

    • run commands and executable files
    • load and execute Beacon Object Files in memory
    • collect system, network, user, domain, and Windows-version details
    • enumerate drives, directories, files, displays, and active user sessions
    • upload, download, copy, move, rename, and delete files
    • capture screenshots every 500 milliseconds, transmitting only changed screen regions after the first full-screen image
    • create processes in another logged-in user’s session
    • operate as a TCP proxy and forward connections
    • remove its persistence and delete its own files

    According to the researchers, the malware is deployed via DLL side-loading after a loader decrypts the RC4-encoded payload contained in a .dat file and maps it directly in memory for evasion.

    The malware features several evasion mechanisms, including call stack and threat origin spoofing, dynamic API resolving, and disguising malicious in-memory code and DLLs as legitimate Windows components.

    To hide from security solutions, SparroWocky is intercepting the Windows thread creation process to alter the start address.

    “SparroWocky uses the MinHook library to hook the CreateThread function in order to conceal the original lpStartAddress parameter from security products.

    “Essentially, any thread created by SparroWocky would have AnimateWindow as the starting address, which would likely be considered legitimate by a security product,” ESET explains.

    SparroWocky establishes persistence either through a Windows service (ProcAuditManager) or by adding a Windows registry key (SnapCart) under HKLM or HKCU, depending on the available privileges.

    The researchers note that the malware’s architecture and evasion techniques “indicate strong knowledge of anti-analysis tricks and Windows internals,” which aligns with their attribution to a well-resourced and experienced threat group.

    While analyzing the attacks, ESET found at least 18 command-and-control (C2) addresses communicating with the malware directly over port 443 or 8080, or through HTTP and SOCKS5 proxies.

    ESET’s telemetry indicates that from mid-2025, FamousSparrow’s focus has been primarily on targets in the Latin America region.

    The company’s report includes a technical analysis of the SparroWocky backdoor and shares a list of indicators of compromise (IoCs) associated with this activity.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat


    Source link

    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    Previous ArticleCisco warns of max severity ISE zero-day exploited in attacks
    Next Article US takes down NightmareStresser DDoS-for-hire platform
    admin
    • Website

    Related Posts

    News

    Malicious npm packages evade install-script defenses at runtime

    September 20, 2026
    News

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026
    News

    Microsoft Teams will let admins block custom file extensions

    September 20, 2026
    Add A Comment

    Comments are closed.

    Demo
    Top Posts

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram
    Latest Reviews
    85
    Featured

    Pico 4 Review: Should You Actually Buy One Instead Of Quest 2?

    January 15, 2021 Featured
    8.1
    Uncategorized

    A Review of the Venus Optics Argus 18mm f/0.95 MFT APO Lens

    January 15, 2021 Uncategorized
    8.9
    Editor's Picks

    DJI Avata Review: Immersive FPV Flying For Drone Enthusiasts

    January 15, 2021 Editor's Picks

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Demo
    Most Popular

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Our Picks

    Malicious npm packages evade install-script defenses at runtime

    September 20, 2026

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026

    Microsoft Teams will let admins block custom file extensions

    September 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook X (Twitter) Instagram Pinterest
    • Home
    • Technology
    • Gaming
    • Phones
    • Buy Now
    © 2026 ThemeSphere. Designed by ThemeSphere.

    Type above and press Enter to search. Press Esc to cancel.