


Close Menu

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026

    Microsoft Teams will let admins block custom file extensions

    September 20, 2026

    Viral AI actress’ hotline face-scans every caller, watches their mood

    September 20, 2026
    Facebook X (Twitter) Instagram
    • Demos
    • Technology
    • Gaming
    • Buy Now
    Facebook X (Twitter) Instagram Pinterest Vimeo
    Canadian Cyber WatchCanadian Cyber Watch
    • Home
    • News
    • Alerts
    • Tips
    • Tools
    • Industry
    • Incidents
    • Events
    • Education
    Subscribe
    Canadian Cyber WatchCanadian Cyber Watch
    Home»News»Iranian hackers use CHOSEN BRICK Windows malware to spy on targets
    News

    Iranian hackers use CHOSEN BRICK Windows malware to spy on targets

    adminBy adminSeptember 16, 2026No Comments3 Mins Read
    Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


    Iranian hackers use CHOSEN BRICK Windows malware to spy on targets

    Government agencies are warning that Iranian state-linked hackers are using a Windows malware strain named CHOSEN BRICK to target dissidents, activists, and journalists worldwide.

    The malware features data theft and espionage capabilities that collect email, Telegram, and WhatsApp communications, take screenshots, and record audio.

    The threat actor primarily targeted individuals in the U.S., U.K., and the Netherlands, whose cybersecurity agencies published a joint advisory with the FBI.

    A typical attack begins with social engineering messages impersonating trusted contacts or technical support agents, sent to targets via WhatsApp or Telegram.

    The threat actor tricks victims into opening malicious files disguised as legitimate applications (e.g., Pictory, RunwayML, Norton Antivirus, Telegram, Adobe Flash Player, KeePass), often suggesting they launch them on personal devices to bypass corporate security blocks.

    Depending on the pretext used, the hackers sometimes used even medical-related lures, the agencies found.
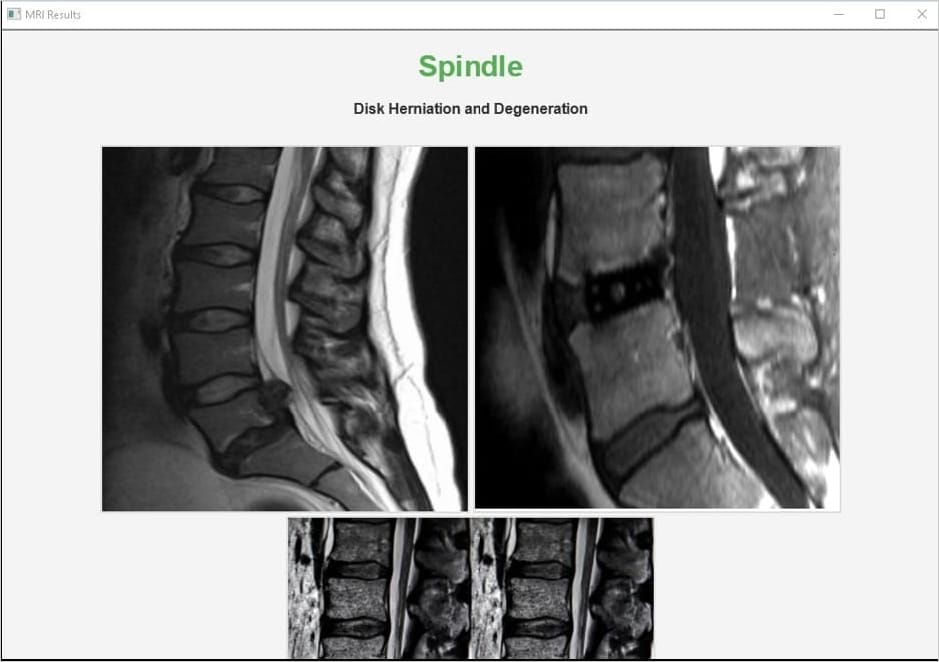
    MRI scan document used as lure
    MRI scan document used as lure
    Source: NCSC

    The apps display a convincing interface that matches the lure, while silently installing CHOSEN BRICK in the background and securing persistence through Windows Registry Run keys.

    The malware adds Microsoft Defender exclusions to evade detection and connects to a unique Telegram bot that matches the victim’s ID and provides command-and-control (C2).

    Once launched, CHOSEN BRICK can perform the following actions:

    • Collect system information
    • Enumerate running processes
    • Capture screenshots
    • Record audio through the microphone
    • Steal email content
    • Steal Telegram or WhatsApp browser data
    • Download additional payloads to “C:\Windows \SysWOW64”
    • Delete files
    • Wipe the entire host system

    The stolen data is exfiltrated through Telegram or cloud services like VultrObjects and StorjShare, while newer CHOSEN BRICK variants route traffic through SOCKS5 proxies to conceal the activity.

    The advisory notes that the stolen data sometimes ends up on pro-Iranian leak sites, serving as a form of harassment and increasing the physical risk for dissidents abroad.

    “Iran almost certainly uses cyber activity to support the repression of individuals who are seen as a threat to the regime, such as dissidents, activists and journalists,” the government agencies say.

    “In some cases, the Iranian intelligence services have plotted to kidnap or conduct lethal operations against individuals internationally, who they perceive as enemies of the regime.”

    Potential victims and organizations should inspect Registry Run entries for suspicious entries, search logs for indicators of compromise (IoCs) shared in the advisory.

    Unexpected connections to Telegram’s API, Backblaze B2, VultrObjects, StorjShare, IPRoyal, and LightningProxies should be investigated as suspicious.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat


    Source link

    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    Previous ArticleWindows 11 KB5124008 update breaks domain trust for some users
    Next Article Anthropic wants Claude to analyze your bank account and financial data
    admin
    • Website

    Related Posts

    News

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026
    News

    Microsoft Teams will let admins block custom file extensions

    September 20, 2026
    News

    Viral AI actress’ hotline face-scans every caller, watches their mood

    September 20, 2026
    Add A Comment

    Comments are closed.

    Demo
    Top Posts

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram
    Latest Reviews
    85
    Featured

    Pico 4 Review: Should You Actually Buy One Instead Of Quest 2?

    January 15, 2021 Featured
    8.1
    Uncategorized

    A Review of the Venus Optics Argus 18mm f/0.95 MFT APO Lens

    January 15, 2021 Uncategorized
    8.9
    Editor's Picks

    DJI Avata Review: Immersive FPV Flying For Drone Enthusiasts

    January 15, 2021 Editor's Picks

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Demo
    Most Popular

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Our Picks

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026

    Microsoft Teams will let admins block custom file extensions

    September 20, 2026

    Viral AI actress’ hotline face-scans every caller, watches their mood

    September 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook X (Twitter) Instagram Pinterest
    • Home
    • Technology
    • Gaming
    • Phones
    • Buy Now
    © 2026 ThemeSphere. Designed by ThemeSphere.

    Type above and press Enter to search. Press Esc to cancel.