

Close Menu

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Webinar: Which Google Workspace security controls actually matter?

    September 20, 2026

    Malicious npm packages evade install-script defenses at runtime

    September 20, 2026

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026
    Facebook X (Twitter) Instagram
    • Demos
    • Technology
    • Gaming
    • Buy Now
    Facebook X (Twitter) Instagram Pinterest Vimeo
    Canadian Cyber WatchCanadian Cyber Watch
    • Home
    • News
    • Alerts
    • Tips
    • Tools
    • Industry
    • Incidents
    • Events
    • Education
    Subscribe
    Canadian Cyber WatchCanadian Cyber Watch
    Home»News»Twitch extension with 30K installs exposes users’ OAuth tokens
    News

    Twitch extension with 30K installs exposes users’ OAuth tokens

    adminBy adminSeptember 14, 2026No Comments3 Mins Read
    Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


    Twitch extension with 30K installs exposes users’ OAuth tokens

    A browser extension called Twitch Enhanced Viewer | JeetBot, available in the official Chrome and Firefox stores, sends users’ Twitch OAuth session tokens to a commercial bot service.

    The extension has more than 30,000 installs and is advertised as a legitimate third-party tool for Twitch that can block ads, force 1080p (full HD) playback, bypass region restrictions, and enable channel-point collection.

    However, an analysis from application security company Socket shows that the extension captures the authorization header used by the Twitch web client, extracts the user OAuth token, and sends the credentials through proxy servers.

    The servers are operated by JeetBot, a commercial Russian-language streaming and chatbot service that offers tools for Twitch, Kick, and VK Live.

    In current versions of the extension, the token is appended directly to redirected proxy requests as an auth= URL parameter, ending up in the proxy server’s request logs, where the software vendor can easily retrieve it.

    “When the extension redirects Twitch’s video playlist request (to usher.ttvnw[.]net) through that proxy, it appends the token as an &auth= query parameter,” Socket says.

    “Because the token is placed in the URL query string, it is written in cleartext into the proxy server’s request logs.”

    This process occurs for every Twitch channel the user watches, except for a set of ten Russian-language channels hardcoded into the extension’s code.
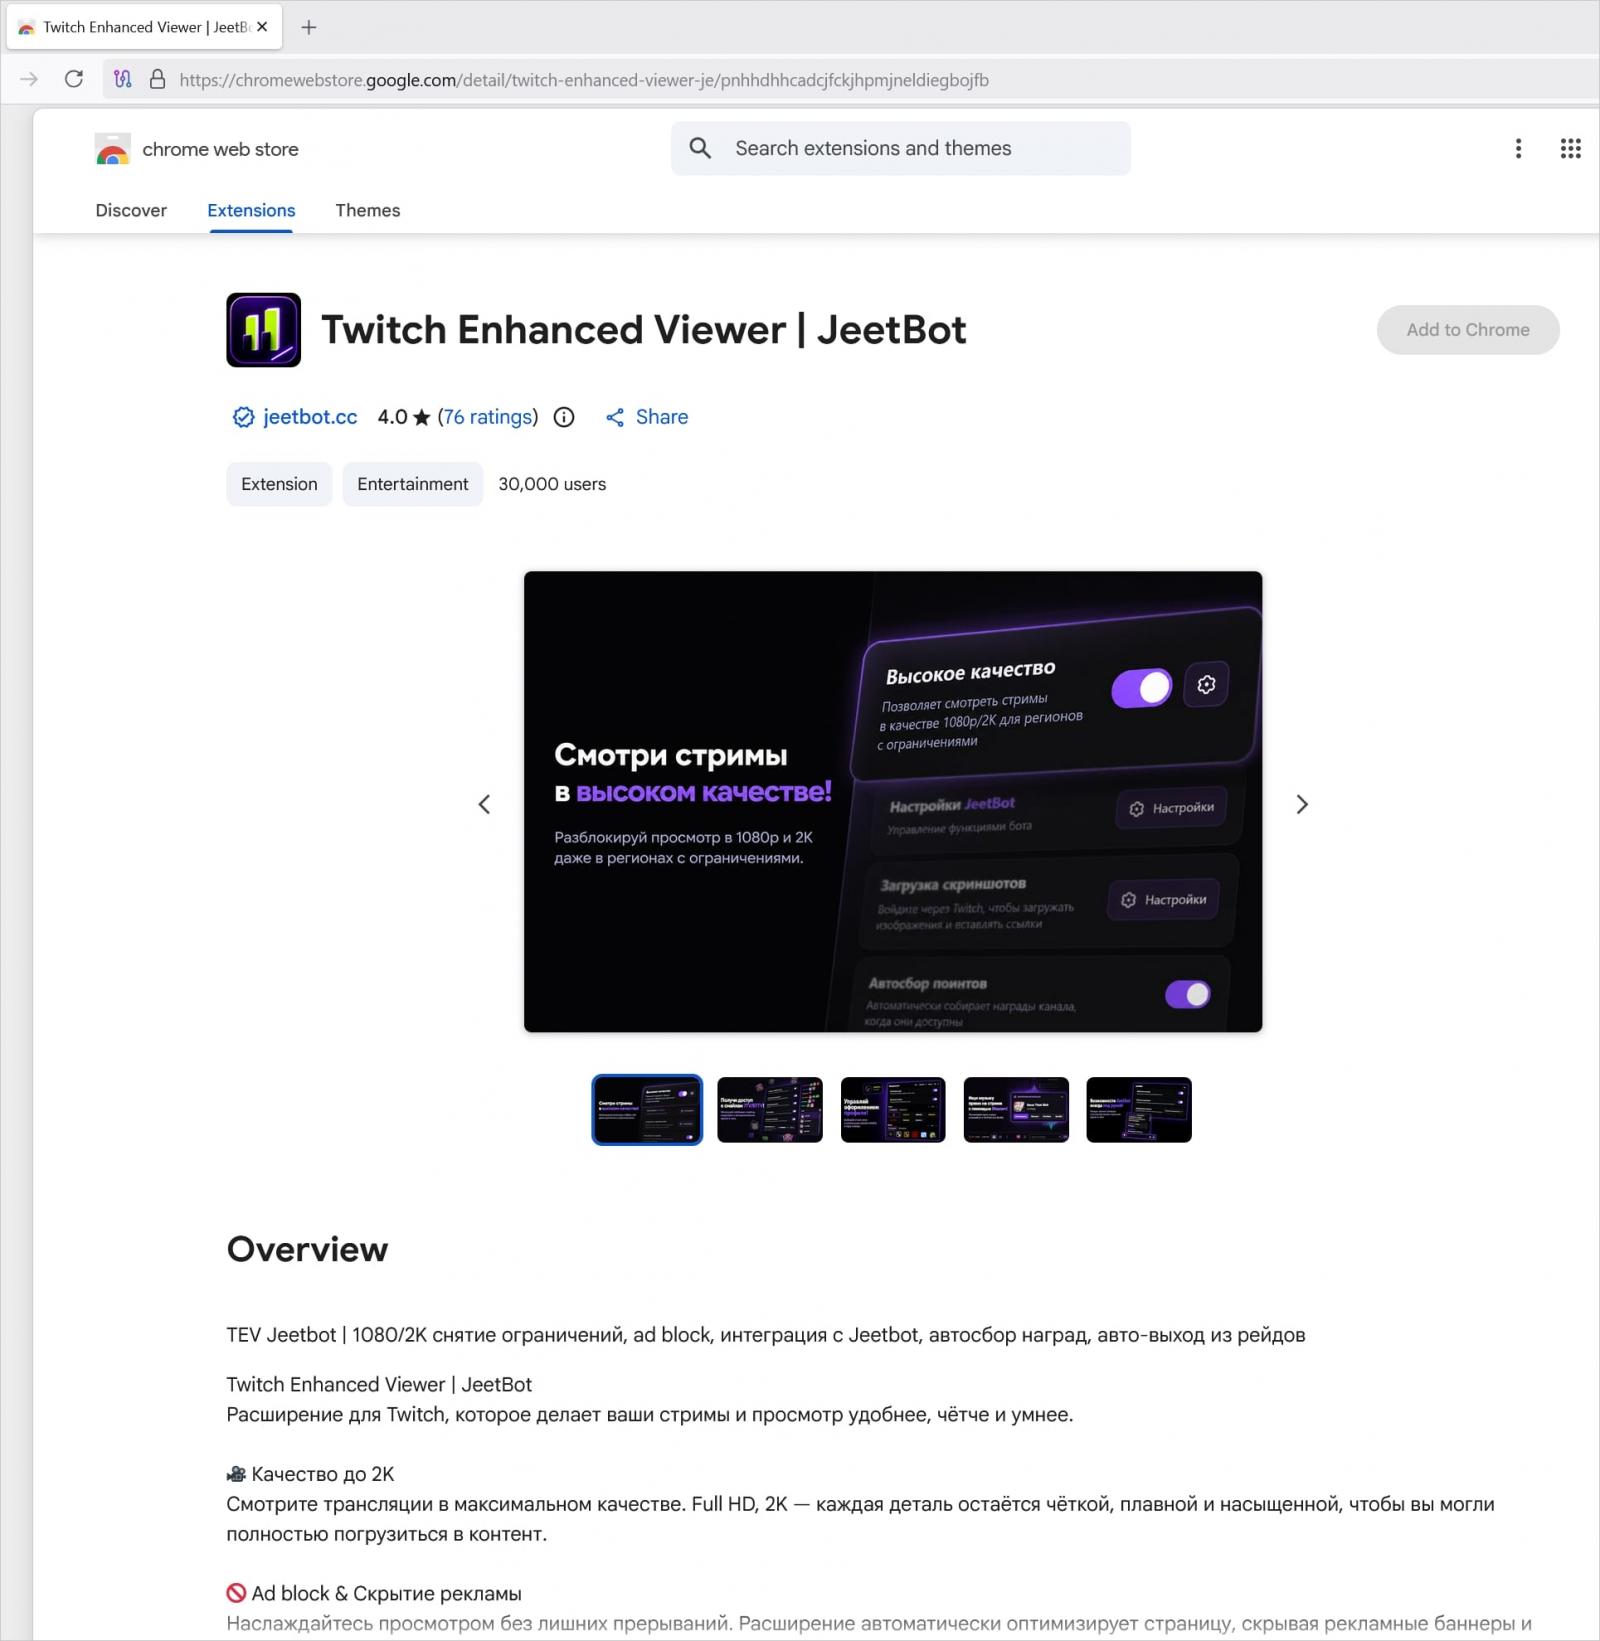
    The malicious extension on the Chrome Web Store
    The malicious extension on the Chrome Web Store
    Source: BleepingComputer.com

    Socket highlights that earlier versions of the extension included more explicit credential-theft mechanisms.

    In the description of the product in the Firefox Add-ons store, the developer provided a disclaimer about the previously used mechanism, saying:

    “Previous versions of the extension transmit your OAuth-twitch token to our server. This is necessary for the stream to run in 1080/1440p.” [machine translated]

    The data privacy disclosure for the Chrome variant of Twitch Enhanced Viewer | JeetBot says that its developer “disclosed that it will not collect or use your data.”

    The declaration covers selling user data to third parties except for approved cases, transferring it for reasons outside the product’s “core functionality,” or “to determine creditworthiness or for lending purposes.”

    At the time of publishing, the extension was still present in both the Chrome Web Store and the Firefox Add-Ons store.

    BleepingComputer has sent JeetBot a request for additional information at the email address indicated in the Chrome Web Store, but we have not received a response by publication.

    Socket researchers believe the extension represents a security risk and recommend that users remove it from their browsers, disconnect all sessions in Twitch, and then re-authenticate, to invalidate any token that may have been forwarded.

    Developers are advised to avoid routing requests with authentication headers or tokens through third-party servers.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat


    Source link

    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    Previous ArticleInfoSec News Nuggets – 09/14/2026 – AboutDFIR
    Next Article New York Seizes 12 Celebrity Deepfake Websites
    admin
    • Website

    Related Posts

    News

    Webinar: Which Google Workspace security controls actually matter?

    September 20, 2026
    News

    Malicious npm packages evade install-script defenses at runtime

    September 20, 2026
    News

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026
    Add A Comment

    Comments are closed.

    Demo
    Top Posts

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram
    Latest Reviews
    85
    Featured

    Pico 4 Review: Should You Actually Buy One Instead Of Quest 2?

    January 15, 2021 Featured
    8.1
    Uncategorized

    A Review of the Venus Optics Argus 18mm f/0.95 MFT APO Lens

    January 15, 2021 Uncategorized
    8.9
    Editor's Picks

    DJI Avata Review: Immersive FPV Flying For Drone Enthusiasts

    January 15, 2021 Editor's Picks

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Demo
    Most Popular

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Our Picks

    Webinar: Which Google Workspace security controls actually matter?

    September 20, 2026

    Malicious npm packages evade install-script defenses at runtime

    September 20, 2026

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook X (Twitter) Instagram Pinterest
    • Home
    • Technology
    • Gaming
    • Phones
    • Buy Now
    © 2026 ThemeSphere. Designed by ThemeSphere.

    Type above and press Enter to search. Press Esc to cancel.