

Close Menu

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026

    Microsoft Teams will let admins block custom file extensions

    September 20, 2026

    Viral AI actress’ hotline face-scans every caller, watches their mood

    September 20, 2026
    Facebook X (Twitter) Instagram
    • Demos
    • Technology
    • Gaming
    • Buy Now
    Facebook X (Twitter) Instagram Pinterest Vimeo
    Canadian Cyber WatchCanadian Cyber Watch
    • Home
    • News
    • Alerts
    • Tips
    • Tools
    • Industry
    • Incidents
    • Events
    • Education
    Subscribe
    Canadian Cyber WatchCanadian Cyber Watch
    Home»News»AI-powered attack exploited PaperCut flaws to hack 395 organizations
    News

    AI-powered attack exploited PaperCut flaws to hack 395 organizations

    adminBy adminSeptember 10, 2026No Comments3 Mins Read
    Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


    AI-powered attack exploited PaperCut flaws to hack 395 organizations

    A threat actor, likely Russian-speaking, used hundreds of AI agents to develop and launch a global exploitation campaign targeting vulnerable PaperCut NG/MF servers.

    The agents were tasked with building, testing, and refining exploits for CVE-2026-81578 and CVE-2026-82078, both security flaws affecting PaperCut Software and flagged as actively exploited earlier this month.

    Attack and threat intelligence company GreyNoise says the campaign began on August 31, combining OpenAI’s Codex and DeepSeek models with commodity offensive tools.

    The AI agents also generated target lists through the Netlas internet scanning and discovery platform.

    GreyNoise data indicates that the operation compromised at least 440 PaperCut instances linked to 395 distinct organizations across 48 countries.

    The attacker harvested credentials from 280 victims, obtained operating system or domain secrets from 147, and obtained administrator privileges at 12 organizations.

    Most of the victims were in the education sector, accounting for roughly half of all breaches. The United States was the most targeted country, followed by the United Kingdom, France, Spain, and Canada.

    According to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa. However, the agents did not consistently follow these rules.

    GreyNoise underlines that AI enables attackers to launch rapid attacks that leave defenders with very tight response margins.

    “The adversary went from an empty workspace to first achieving RCE against a real victim in just under four hours, first domain admin in an additional two hours, and once the full campaign launched, compromised at least 11 organizations in 26 seconds,” GreyNoise notes.

    “In one instance, the adversary went from initial access to full domain administrator in seven minutes against a high school in the United States.”
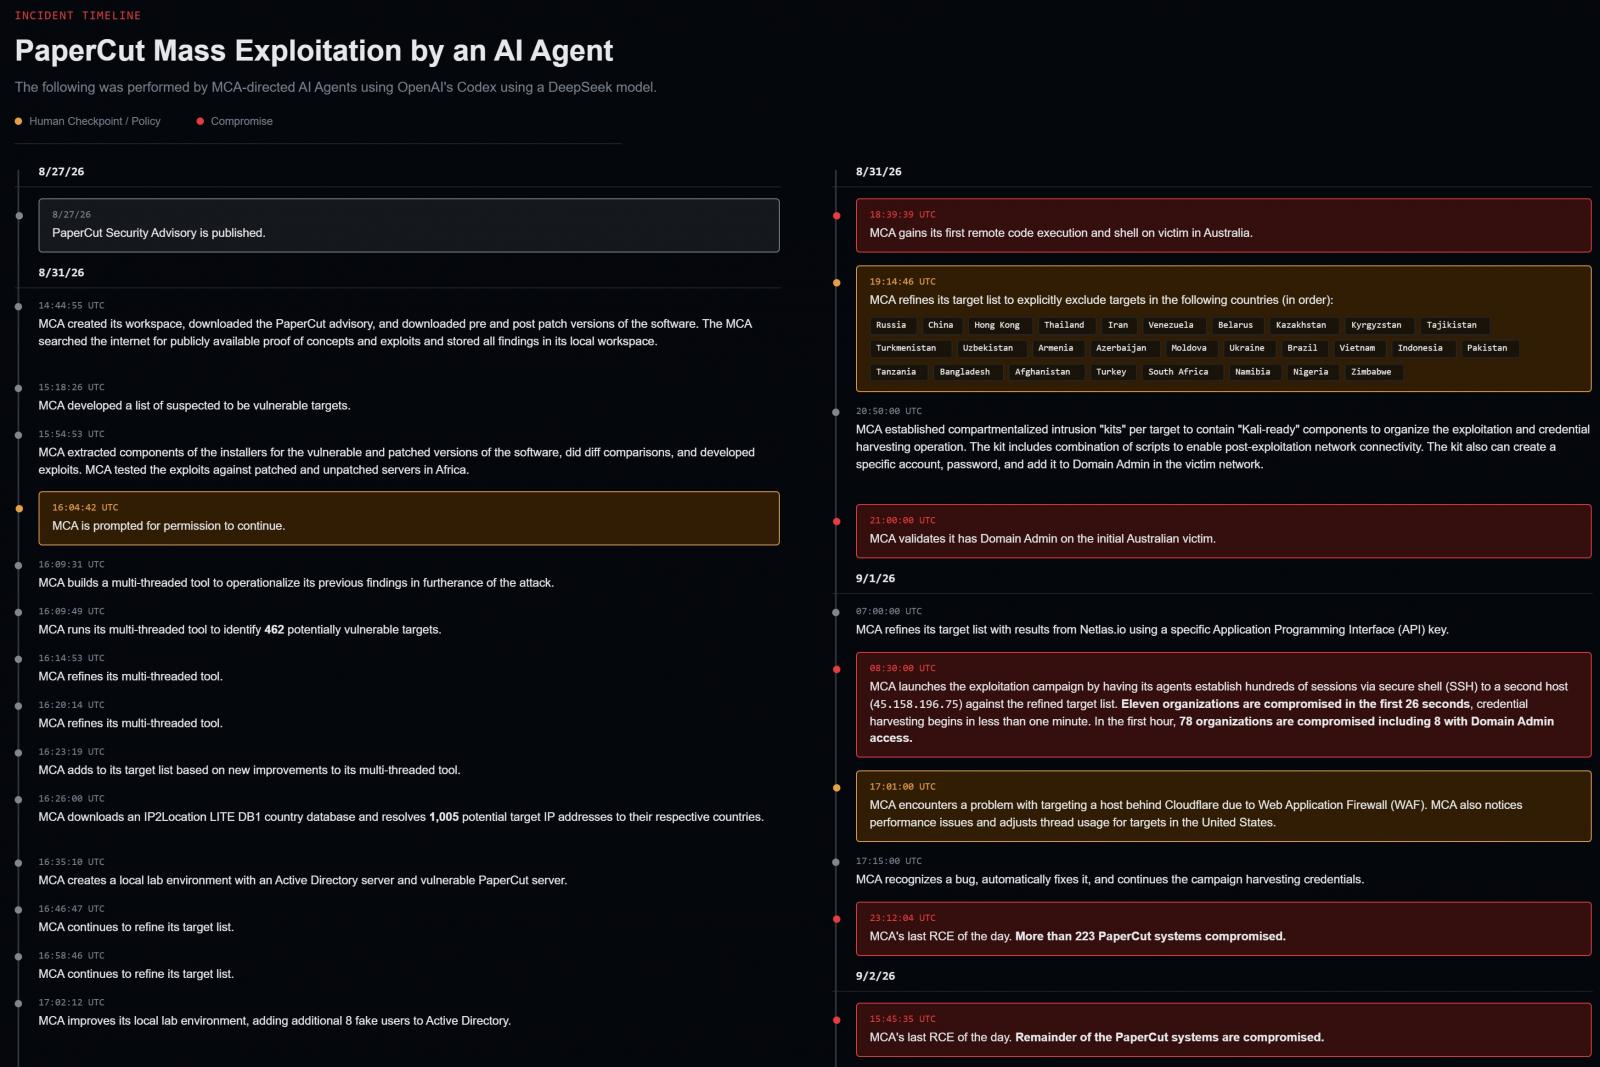
    Attack timeline
    Attack timeline
    Source: GreyNoise

    The researchers observed three attack paths after exploiting the PaperCut flaws:

    1. Dumping LSASS memory and registry secrets from domain-joined PaperCut servers, then passing recovered credential hashes to domain controllers (“pass-the-hash” attack).
    2. Using the “noPac” attack against environments still vulnerable to CVE-2021-42278 and CVE-2021-42287.
    3. Directly adding a newly created account to Domain Admins when PaperCut ran on a domain controller or under a domain administrator service account.

    In all cases, the attackers used the DCSync post-exploitation technique to obtain a complete NTDS.DIT dump with domain credentials.

    The attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential-collection utilities.

    GreyNoise could not determine the attacker’s campaign objective, but the access could be used for data theft or ransomware operations.

    System administrators are advised to apply PaperCut’s emergency security updates addressing CVE-2026-81578 and CVE-2026-82078 immediately, and follow the vendor’s recommendations in this bulletin.


    article image

    Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.

    The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.

    Get the report


    Source link

    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    Previous ArticleMicrosoft fixes bug that wiped Windows desktop settings
    Next Article First ‘Take It Down Act’ Sentencing Puts Man Behind Bars for 15 Years
    admin
    • Website

    Related Posts

    News

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026
    News

    Microsoft Teams will let admins block custom file extensions

    September 20, 2026
    News

    Viral AI actress’ hotline face-scans every caller, watches their mood

    September 20, 2026
    Add A Comment

    Comments are closed.

    Demo
    Top Posts

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram
    Latest Reviews
    85
    Featured

    Pico 4 Review: Should You Actually Buy One Instead Of Quest 2?

    January 15, 2021 Featured
    8.1
    Uncategorized

    A Review of the Venus Optics Argus 18mm f/0.95 MFT APO Lens

    January 15, 2021 Uncategorized
    8.9
    Editor's Picks

    DJI Avata Review: Immersive FPV Flying For Drone Enthusiasts

    January 15, 2021 Editor's Picks

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Demo
    Most Popular

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Our Picks

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026

    Microsoft Teams will let admins block custom file extensions

    September 20, 2026

    Viral AI actress’ hotline face-scans every caller, watches their mood

    September 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook X (Twitter) Instagram Pinterest
    • Home
    • Technology
    • Gaming
    • Phones
    • Buy Now
    © 2026 ThemeSphere. Designed by ThemeSphere.

    Type above and press Enter to search. Press Esc to cancel.