

Close Menu

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Webinar: Which Google Workspace security controls actually matter?

    September 20, 2026

    Malicious npm packages evade install-script defenses at runtime

    September 20, 2026

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026
    Facebook X (Twitter) Instagram
    • Demos
    • Technology
    • Gaming
    • Buy Now
    Facebook X (Twitter) Instagram Pinterest Vimeo
    Canadian Cyber WatchCanadian Cyber Watch
    • Home
    • News
    • Alerts
    • Tips
    • Tools
    • Industry
    • Incidents
    • Events
    • Education
    Subscribe
    Canadian Cyber WatchCanadian Cyber Watch
    Home»News»ENISA’s CRA Single Reporting Platform Just Went Live. Here’s What You Actually Need to Know. | Blog
    News

    ENISA’s CRA Single Reporting Platform Just Went Live. Here’s What You Actually Need to Know. | Blog

    adminBy adminSeptember 14, 2026No Comments3 Mins Read
    Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


    September 11, 2026, the Cyber Resilience Act’s (CRA) reporting obligations officially kicked in, and ENISA’s Single Reporting Platform (SRP) went live right alongside them.
    If you’re a manufacturer of products with digital elements sold in the EU, this is the tool you now have to use to report actively exploited vulnerabilities and severe incidents. In this post I’ll break down who has to report, what you’re actually obligated to report and when the clocks start ticking, and walk through the new platform itself.
    Who Has to Report

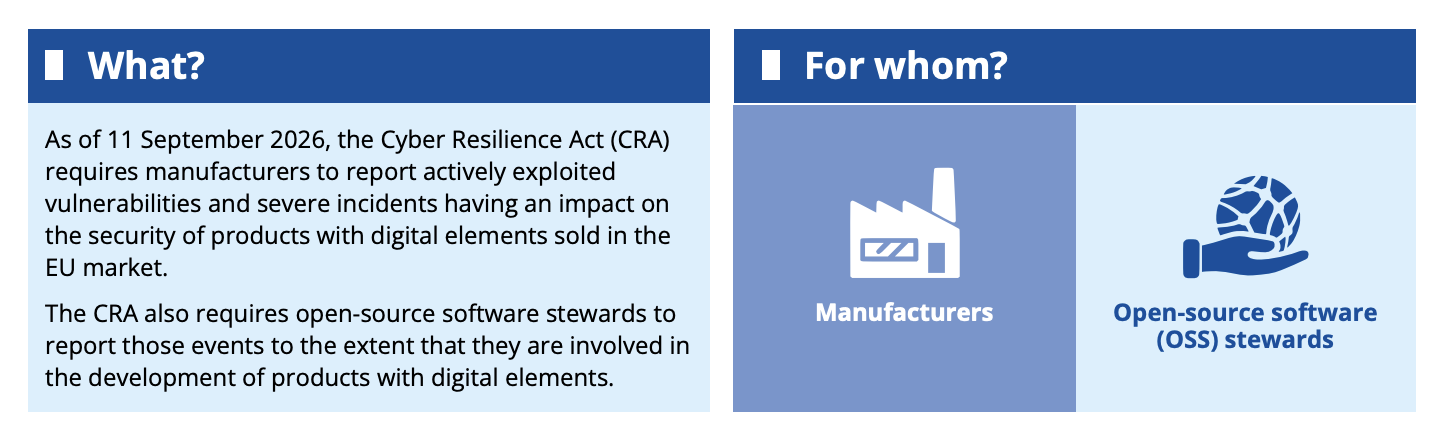
    As of today, the CRA requires manufacturers to report actively exploited vulnerabilities and severe incidents impacting the security of products with digital elements sold in the EU market.
    Open-source software stewards are also on the hook, but only to the extent they’re involved in the development of products with digital elements.
    Who Has to Report

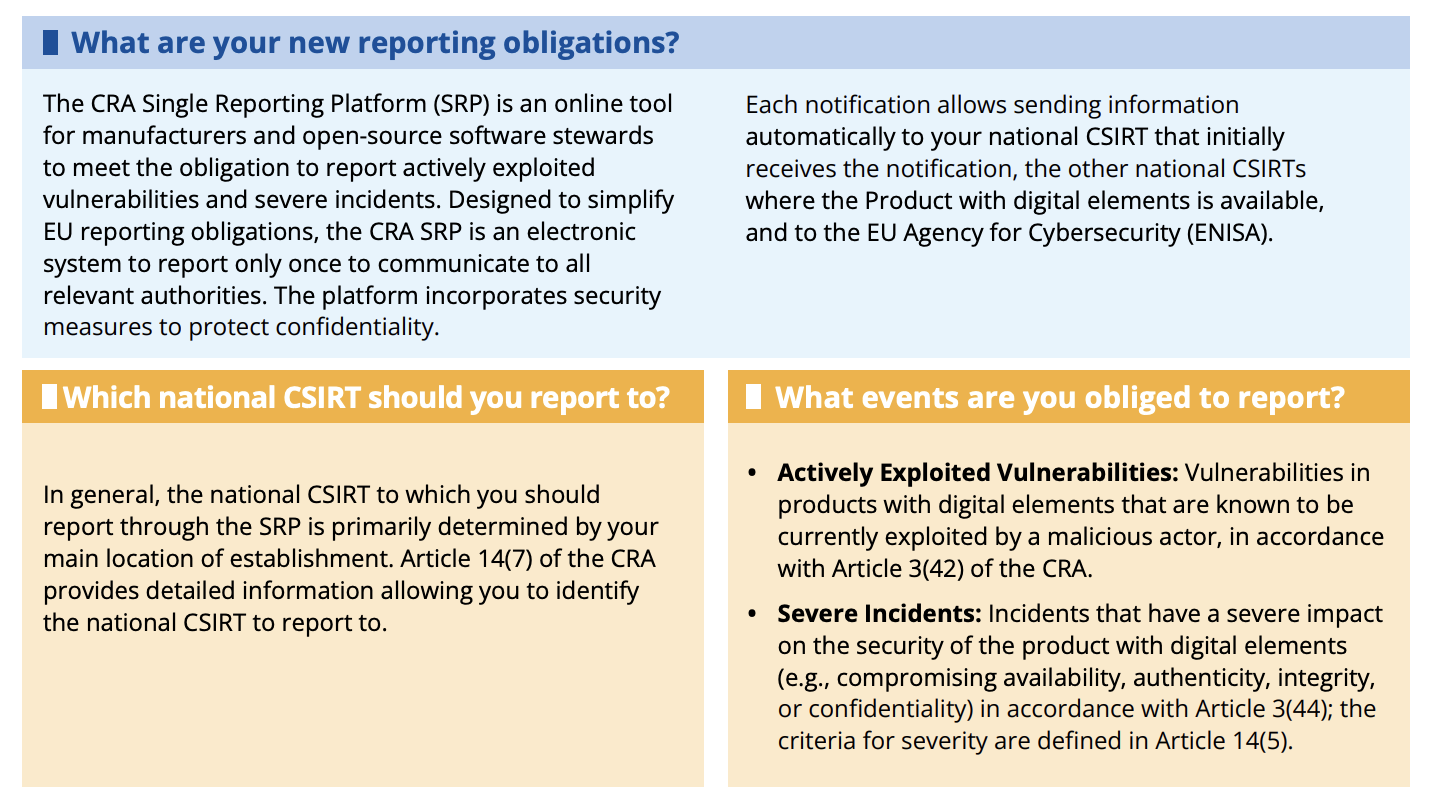
    Manufactures are required to report two things:

    1. Actively exploited vulnerabilities: a vulnerability in a product with digital elements that is known to be exploited by a malicious actor, per Article 3(42).
    2. Severe incidents: incidents that have a severe impact on the security of a product with digital elements (think: compromised availability, authenticity, integrity, or confidentiality), per Article 3(44). The severity criteria itself is spelled out in Article 14(5).

    This is one of the first questions the platform asks you, and it trips people up. Article 14(7) lays out the logic, but here’s the TL;DR:

    Report to the CSIRT where decisions related to your cybersecurity products are made. If you’re not based in the EU, work down this list based on the Member State with:

    1. The highest number of products with digital elements where the manufacturer is established
    2. The importer placing the highest number of products on the market
    3. The distributor making available the highest number of products
    4. The highest number of users of the product
    Who Has to Report

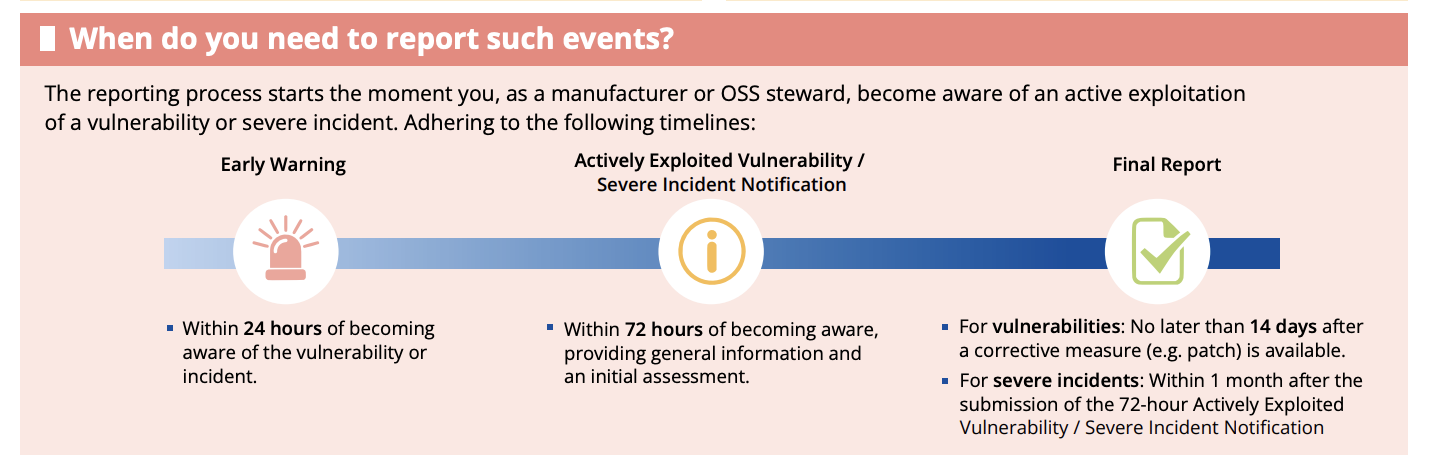
    The clock starts the moment you become aware:

    • 24 hours: submit an early warning
    • 72 hours: provide general information and an initial assessment
    • Final report:

      • For vulnerabilities: 14 days after a corrective measure becomes available
      • For severe incidents: within 1 month of the 72-hour notification

    Missing these deadlines you out of compliance with one of the CRA’s first deadlines.

    ENISA’s Single Reporting Platform(SRP)

    Single Reporting Platform Resources

    Single Reporting Platform FAQ

    VulnCheck KEV provides timely visibility and evidence into vulnerabilities being exploited in the wild. Sign up for free community access and alerting today at https://www.vulncheck.com/kev

    VulnCheck Canary Intelligence provides additional insight into actively exploited vulnerabilities such as who is exploiting what, the source Hosts/IPs of the attacker, C2 infrastructure and additional techniques and tactics used in the attack.

    VulnCheck is helping organizations not just to solve the vulnerability prioritization challenge – we’re working to help equip any product manager, CSIRT/PSIRT or SecOps team and Threat Hunting team to get faster and more accurate with infinite efficiency using VulnCheck solutions.

    We knew that we needed better data, faster across the board, in our industry. So that’s what we deliver to the market. We’re going to continue to deliver key insights on vulnerability management, exploitation and major trends we can extrapolate from our dataset to continuously support practitioners.

    Are you interested in learning more? If so, VulnCheck’s Exploit & Vulnerability Intelligence has broad threat actor coverage. Register and demo our data today.


    Source link

    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    Previous ArticleNew York Seizes 12 Celebrity Deepfake Websites
    Next Article Cops Search Thousands of Flock Cameras for Reasons of ‘LMAO,’ ‘IDK,’ ‘Hehe,’ and ‘asdfg’
    admin
    • Website

    Related Posts

    News

    Webinar: Which Google Workspace security controls actually matter?

    September 20, 2026
    News

    Malicious npm packages evade install-script defenses at runtime

    September 20, 2026
    News

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026
    Add A Comment

    Comments are closed.

    Demo
    Top Posts

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram
    Latest Reviews
    85
    Featured

    Pico 4 Review: Should You Actually Buy One Instead Of Quest 2?

    January 15, 2021 Featured
    8.1
    Uncategorized

    A Review of the Venus Optics Argus 18mm f/0.95 MFT APO Lens

    January 15, 2021 Uncategorized
    8.9
    Editor's Picks

    DJI Avata Review: Immersive FPV Flying For Drone Enthusiasts

    January 15, 2021 Editor's Picks

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Demo
    Most Popular

    Catchy & Intriguing

    March 17, 202679 Views

    How fraudsters target credit unions

    May 4, 202644 Views

    IP Address Investigations and Local OSINT

    March 20, 202641 Views
    Our Picks

    Webinar: Which Google Workspace security controls actually matter?

    September 20, 2026

    Malicious npm packages evade install-script defenses at runtime

    September 20, 2026

    Researchers escape OpenAI Codex sandbox to run commands on host

    September 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook X (Twitter) Instagram Pinterest
    • Home
    • Technology
    • Gaming
    • Phones
    • Buy Now
    © 2026 ThemeSphere. Designed by ThemeSphere.

    Type above and press Enter to search. Press Esc to cancel.