Close Menu

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Black Hat USA 2026 | Trusted Enough to Run: Breaking AI Agents in Official Workflows

    November 22, 2026

    Black Hat USA 2026 | Anatomy of a Takedown: Inside the Operation That Broke LockBit

    November 21, 2026

    DEF CON CTF Walkthrough: Web Exploitation

    November 20, 2026
    Facebook X (Twitter) Instagram
    • Demos
    • Technology
    • Gaming
    • Buy Now
    Facebook X (Twitter) Instagram Pinterest Vimeo
    Canadian Cyber WatchCanadian Cyber Watch
    • Home
    • News
    • Alerts
    • Tips
    • Tools
    • Industry
    • Incidents
    • Events
    • Education
    Subscribe
    Canadian Cyber WatchCanadian Cyber Watch
    Home»News»Misconfigured Supabase apps expose data in over 16,000 databases
    News

    Misconfigured Supabase apps expose data in over 16,000 databases

    adminBy adminSeptember 28, 2026No Comments3 Mins Read
    Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
    Share
    Facebook Twitter LinkedIn Pinterest Email


    Over 16,000 Supabase databases expose PII, passwords, auth tokens

    Researchers found more than 16,000 misconfigured Supabase databases exposing readable tables with personally identifiable information, passwords, or authentication tokens.

    Based on the analysis of table schemas, researchers at cyber risk management company UpGuard believe that a very small set of the exposed information includes credit card data.

    Supabase is an open-source development platform built around PostgreSQL that provides developers with a range of backend services to build and launch apps and websites faster.

    The service has become increasingly popular among developers using artificial intelligence tools to build projects, with AI-assisted development accounting for more than 60% of newly created databases.

    UpGuard researchers analyzed a dataset of around 300,000 domains that showed signs of using Supabase and checked for a ‘users’ table. While some queries returned a page from the database, others hinted that the ‘users’ table did not exist, but a table with another name was accessible.

    The researchers then used the table schemas to infer the data types exposed across the set. In more than half of the exposed databases, UpGuard found personally identifiable information (PII), with a smaller subset including passwords and authentication tokens.
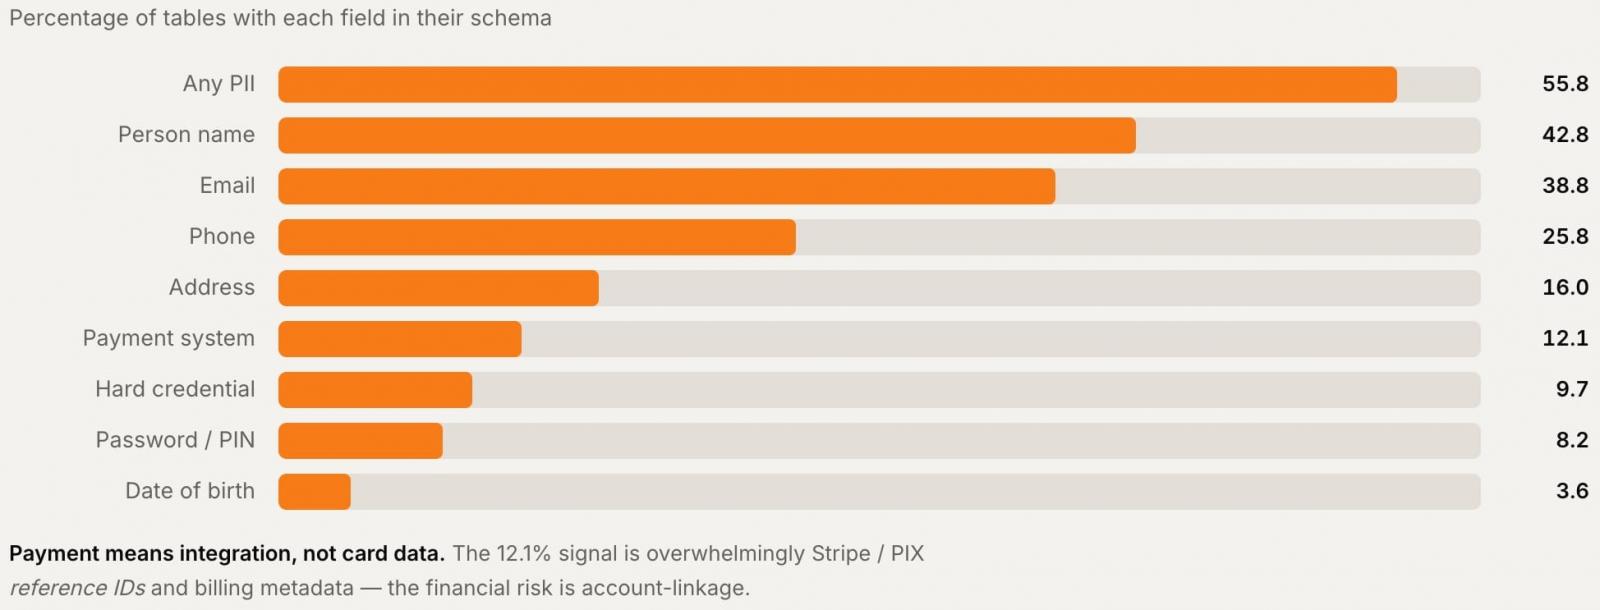
    Exposed data types
    Exposed data types
    Source: UpGuard

    Among the more notable findings was a U.S. valet service that exposed more than 100,000 customer records, including contact details, license plates, and visit history.

    At a Canadian immigration service, the researchers said they found nearly 5,000 user records, including 884 plaintext passwords.

    Sensitive identity, payment accounts, and over 100,000 private messages were found at an India-based adult creator platform, UpGuard says.

    A Philippines-based OTP service exposed data on more than 2,000 users and 100,000 SMS messages, including some apparently unrelated person-to-person communications.

    An African government consulate exposed records belonging to 25,000 people, including addresses and emergency housing locations.

    The researchers attribute the exposure to poor application security configurations, including missing or ineffective row-level security policies and misuse of public keys.

    UpGuard explained that the security issues are not limited to a particular type of business:

    “The security settings are invariant to business type because the humans, who know what kind of business they are advertising, do not understand their database’s configuration,” UpGuard explains.

    “The common thread is that these sites are created by AI coding agents and the humans are unaware of the configuration.”

    Despite highlighting the increased risk of misconfigurations with AI-assisted app development, the researchers stressed that their scans do not establish that every affected site was built using an AI coding agent.

    UpGuard said it notified application owners when its deeper analysis identified significant exposure.

    Supabase users are encouraged to review the platform’s security documentation, including its advisors and API security guide, to identify exposure risks and mitigate them.


    article image

    Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.

    Save your seat


    Source link

    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
    Previous ArticleHumans Are Reading Copilot Prompts — And They’re Horrified
    Next Article Japan’s Keio confirms ransomware attack disrupted business systems
    admin
    • Website

    Related Posts

    News

    JCTables for Joomla: When “Already Escaped” Means Injectable | Blog

    October 1, 2026
    News

    Vulnerability Discovery and Exploitation Trends in the AI Era

    October 1, 2026
    News

    Microsoft is rolling out Linux container support to WSL

    September 30, 2026
    Add A Comment

    Comments are closed.

    Demo
    Top Posts

    Catchy & Intriguing

    March 17, 202684 Views

    How to prove false statements? (Part 3)

    March 24, 202668 Views

    The Package That Never Was: How Delivery Service Scams Are Fooling Canadians

    April 1, 202665 Views
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram
    Latest Reviews
    85
    Featured

    Pico 4 Review: Should You Actually Buy One Instead Of Quest 2?

    January 15, 2021 Featured
    8.1
    Uncategorized

    A Review of the Venus Optics Argus 18mm f/0.95 MFT APO Lens

    January 15, 2021 Uncategorized
    8.9
    Editor's Picks

    DJI Avata Review: Immersive FPV Flying For Drone Enthusiasts

    January 15, 2021 Editor's Picks

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Demo
    Most Popular

    Catchy & Intriguing

    March 17, 202684 Views

    How to prove false statements? (Part 3)

    March 24, 202668 Views

    The Package That Never Was: How Delivery Service Scams Are Fooling Canadians

    April 1, 202665 Views
    Our Picks

    Black Hat USA 2026 | Trusted Enough to Run: Breaking AI Agents in Official Workflows

    November 22, 2026

    Black Hat USA 2026 | Anatomy of a Takedown: Inside the Operation That Broke LockBit

    November 21, 2026

    DEF CON CTF Walkthrough: Web Exploitation

    November 20, 2026

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    Facebook X (Twitter) Instagram Pinterest
    • Home
    • Technology
    • Gaming
    • Phones
    • Buy Now
    © 2026 ThemeSphere. Designed by ThemeSphere.

    Type above and press Enter to search. Press Esc to cancel.